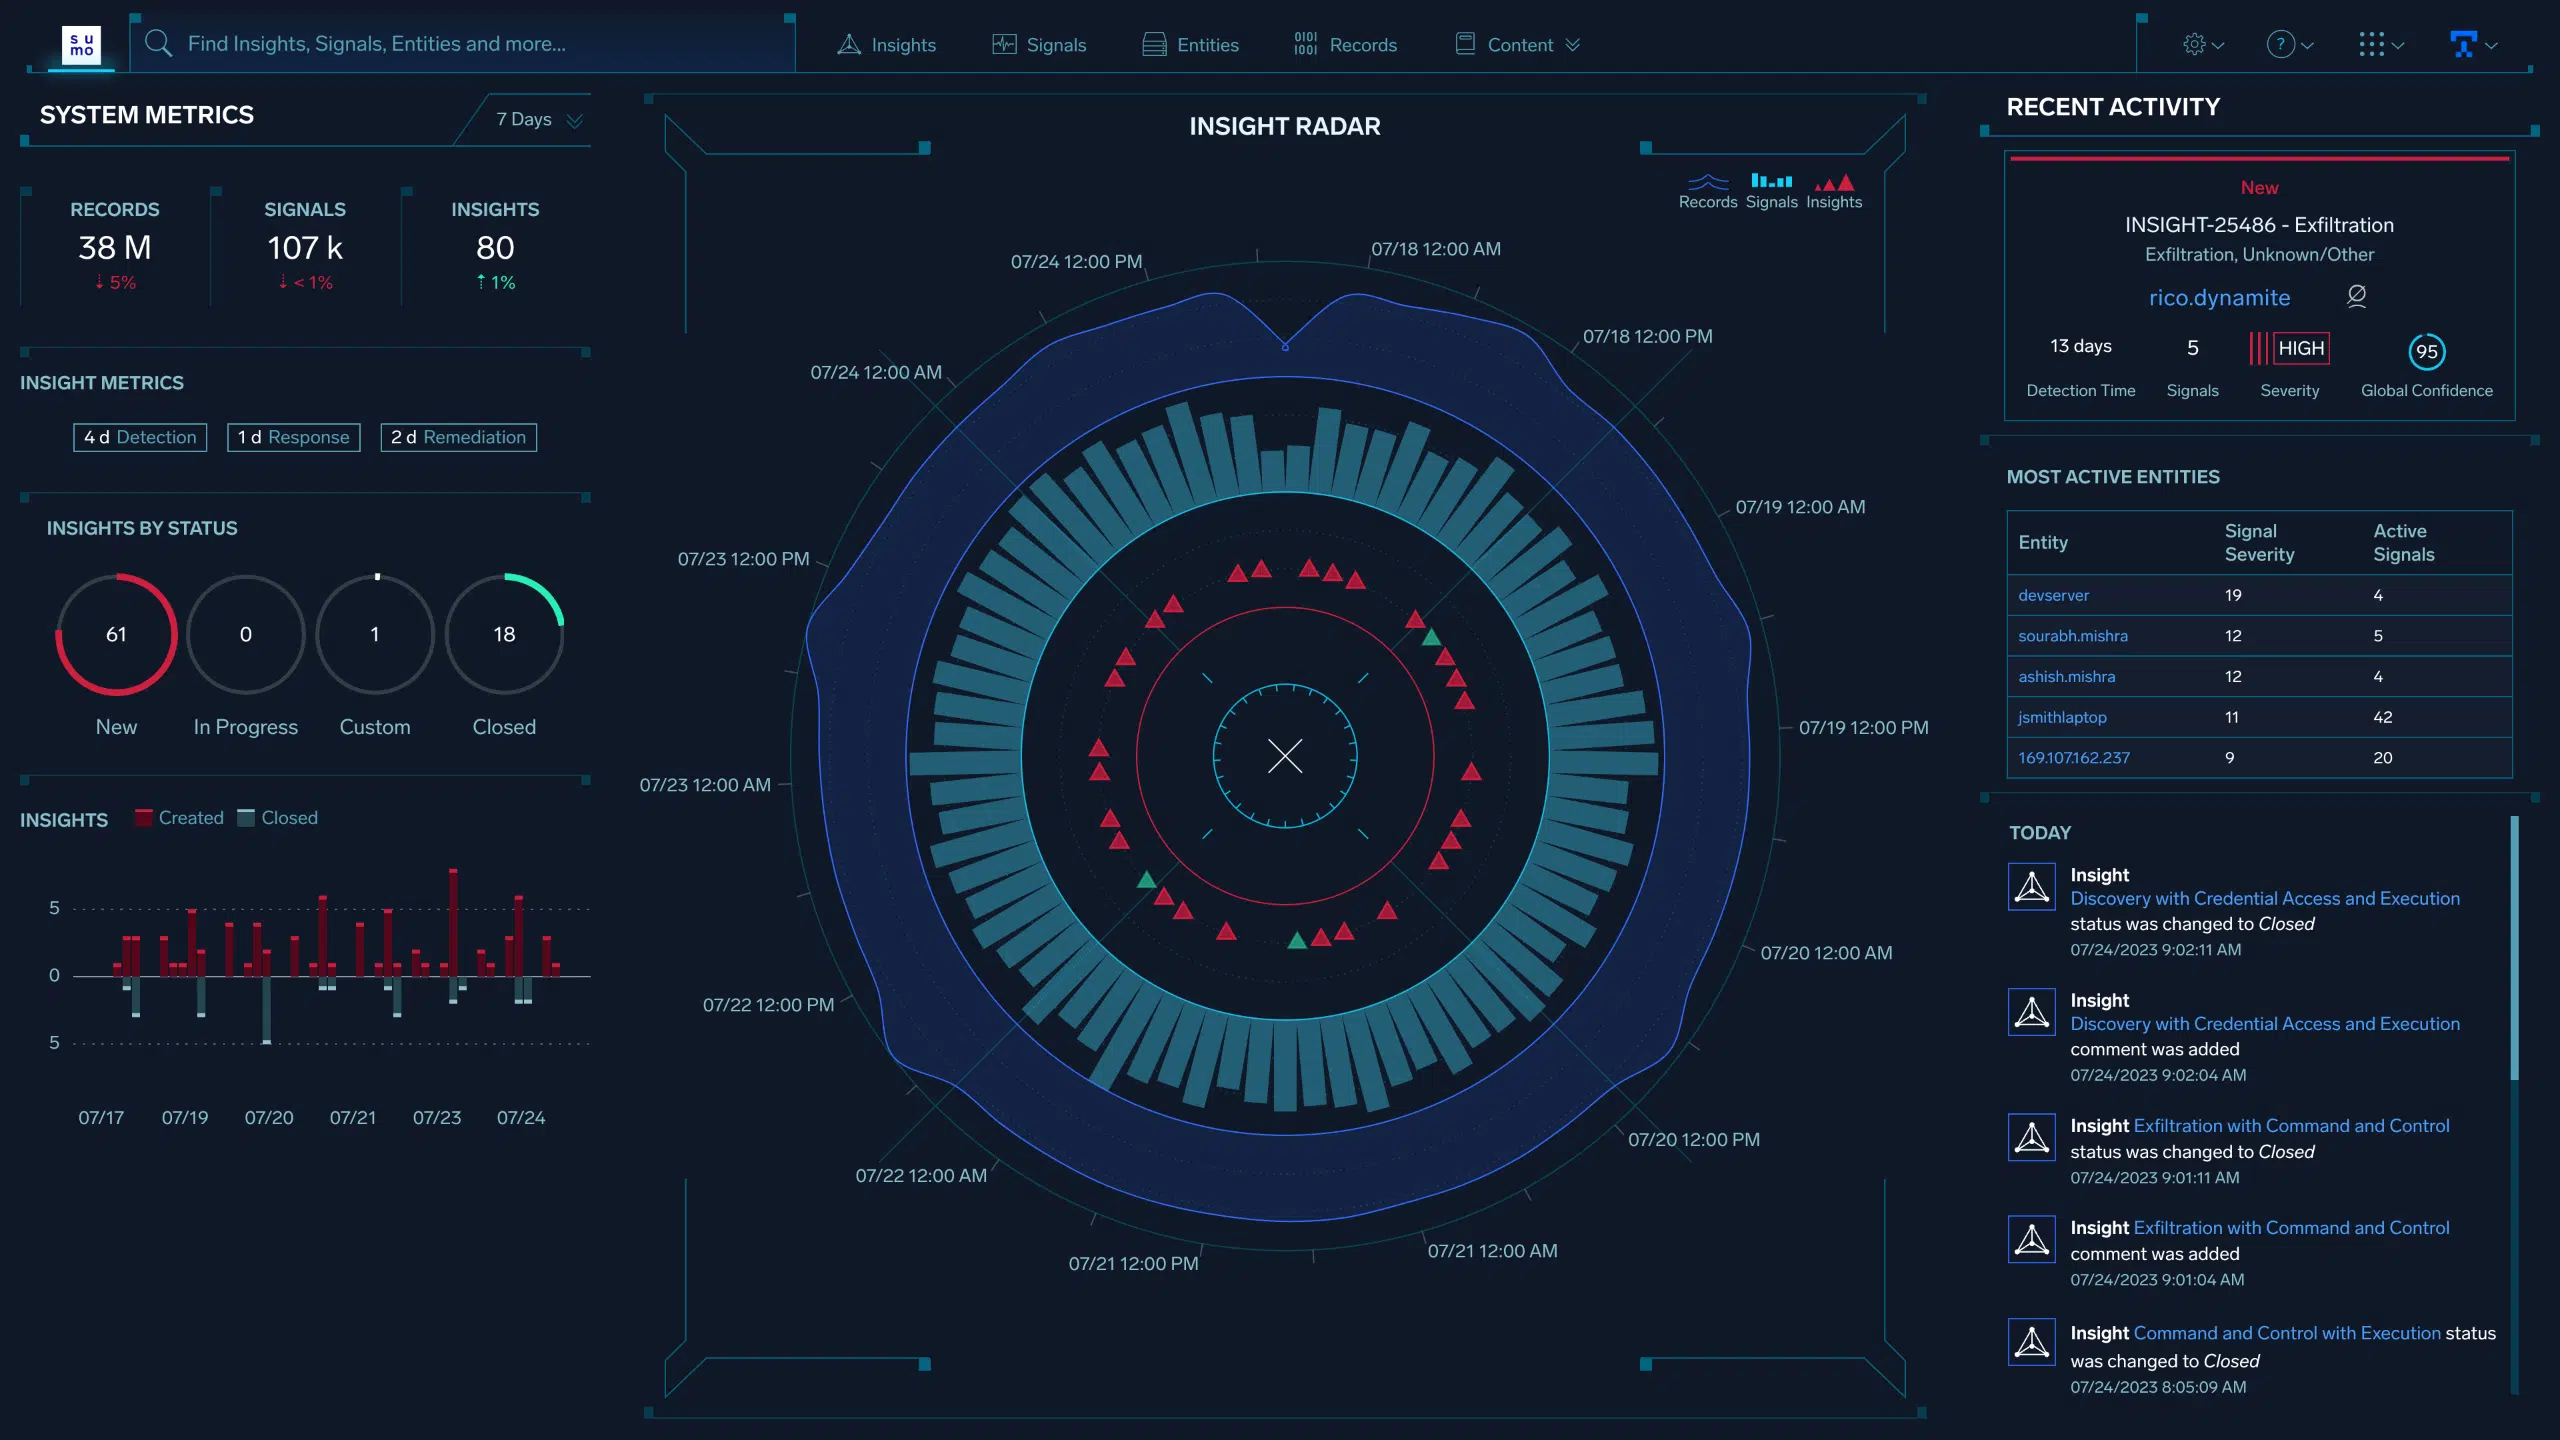
脅威がビジネスを妨害する前にこちらから脅威を阻止します

世界中で2,500社以上のお客様から信頼されています

Alaska Airlines logo
Dolby logo
Grammarly logo
Hello Fresh logo
Samsung logo
Ulta Beauty logo

AI SOC 対 ホワイトボックスAI

あらゆるものを自律化すると約束する「AI SOC」スタートアップの波が高まっています。これらのスタートアップは、アラートの優先順位付け、脅威の調査、さらにはプレイブックの実行まで行います。ボタンを押せば、あとは機械に任せて、魔法のように面倒が片付くというわけです。

sl n4iietdfjfgt
sl n4iietdfjfgt
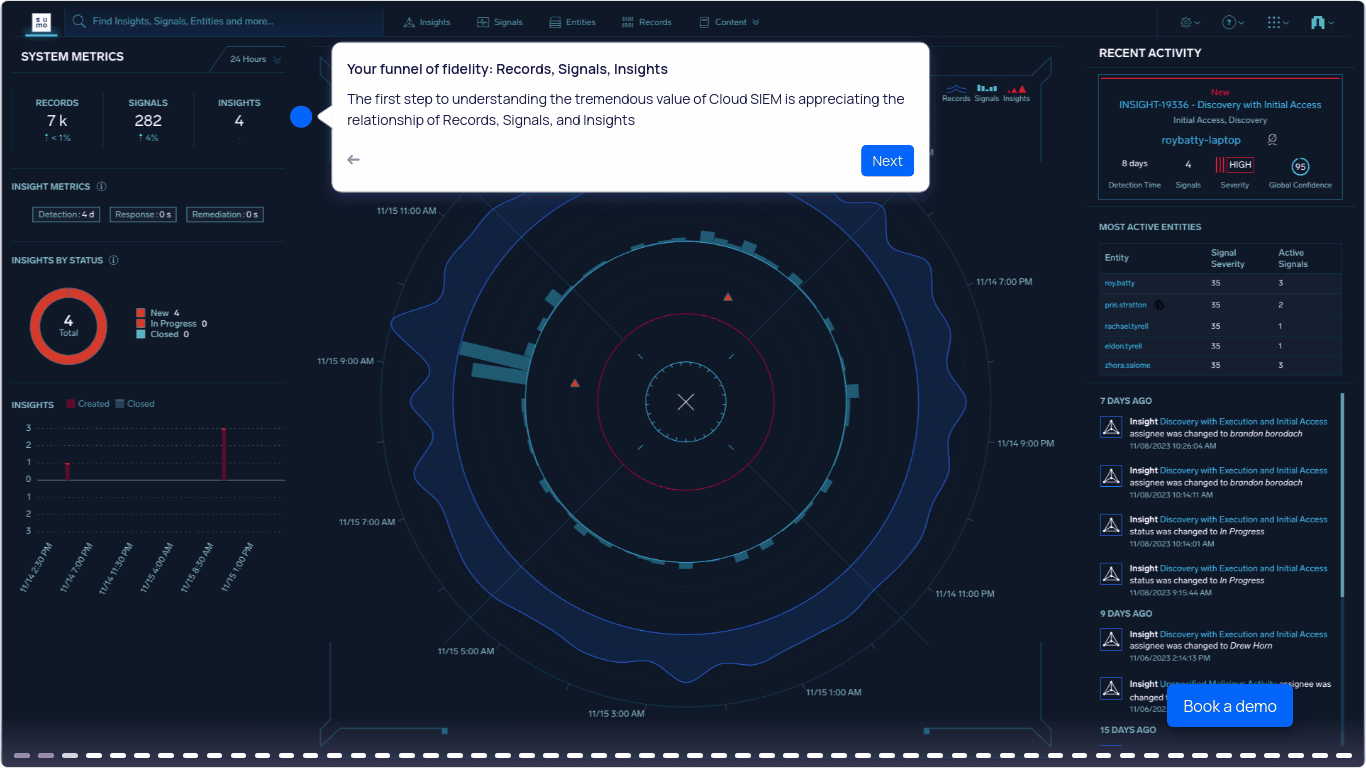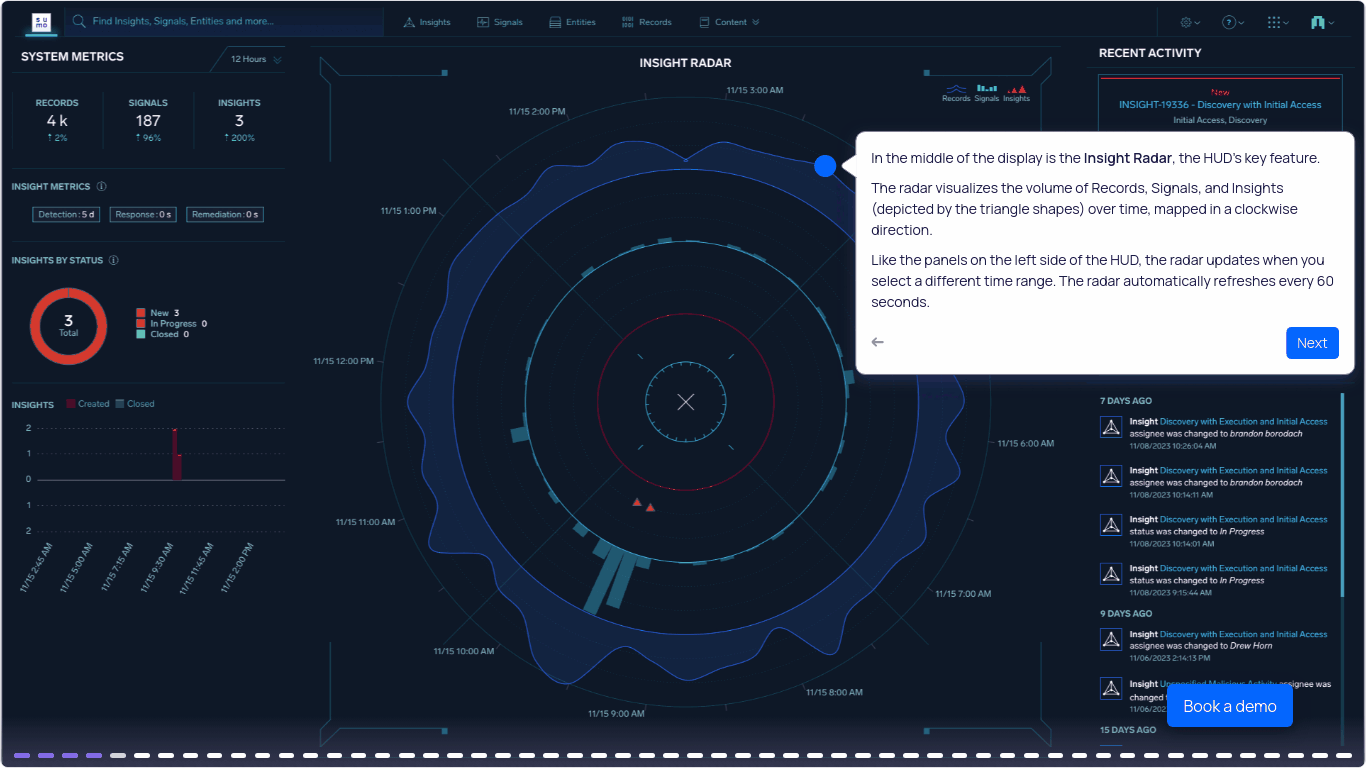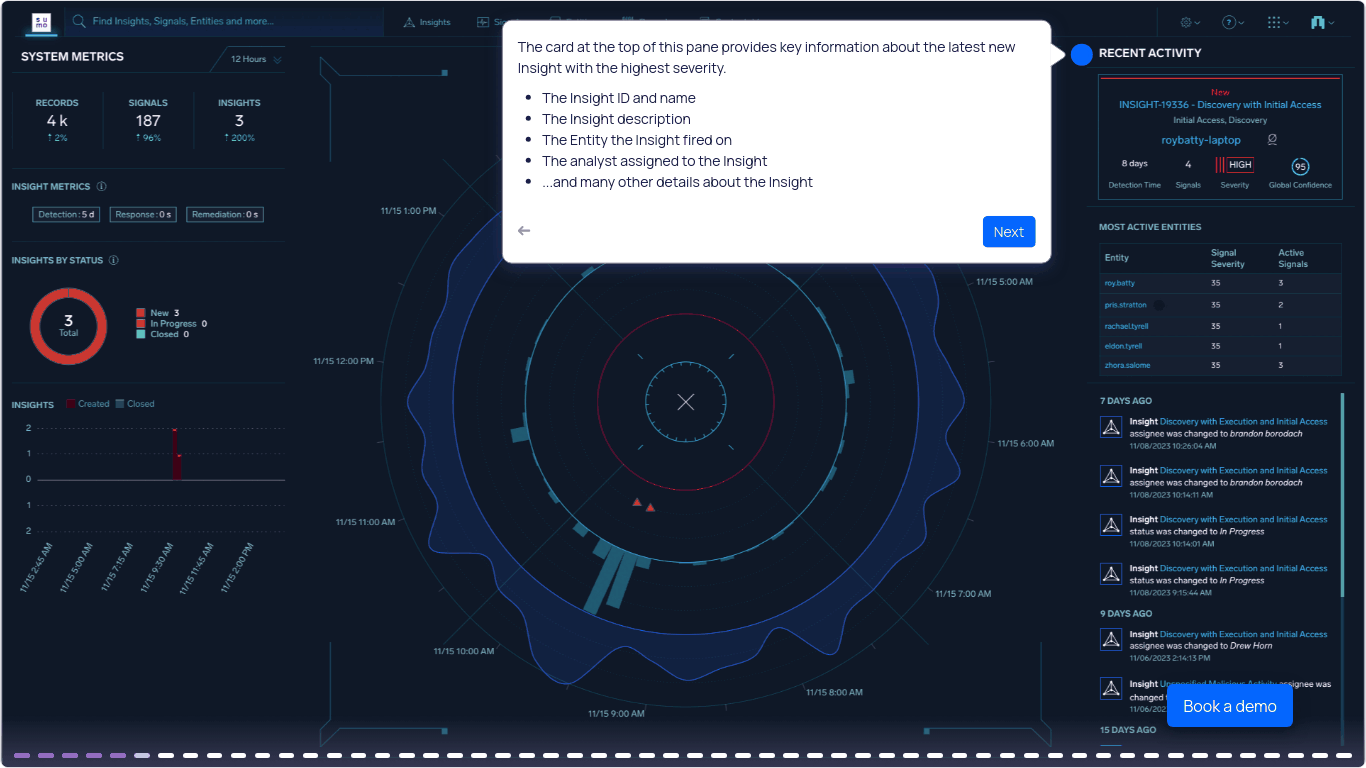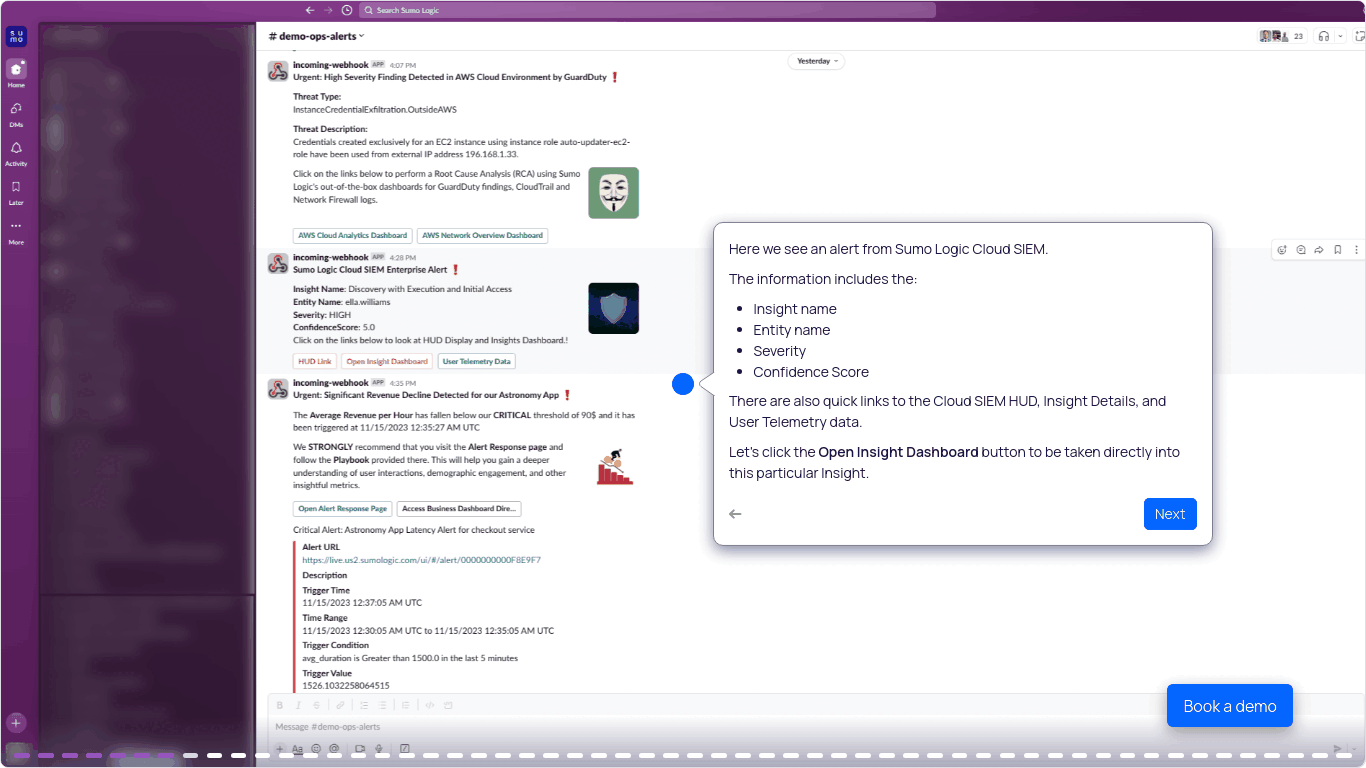
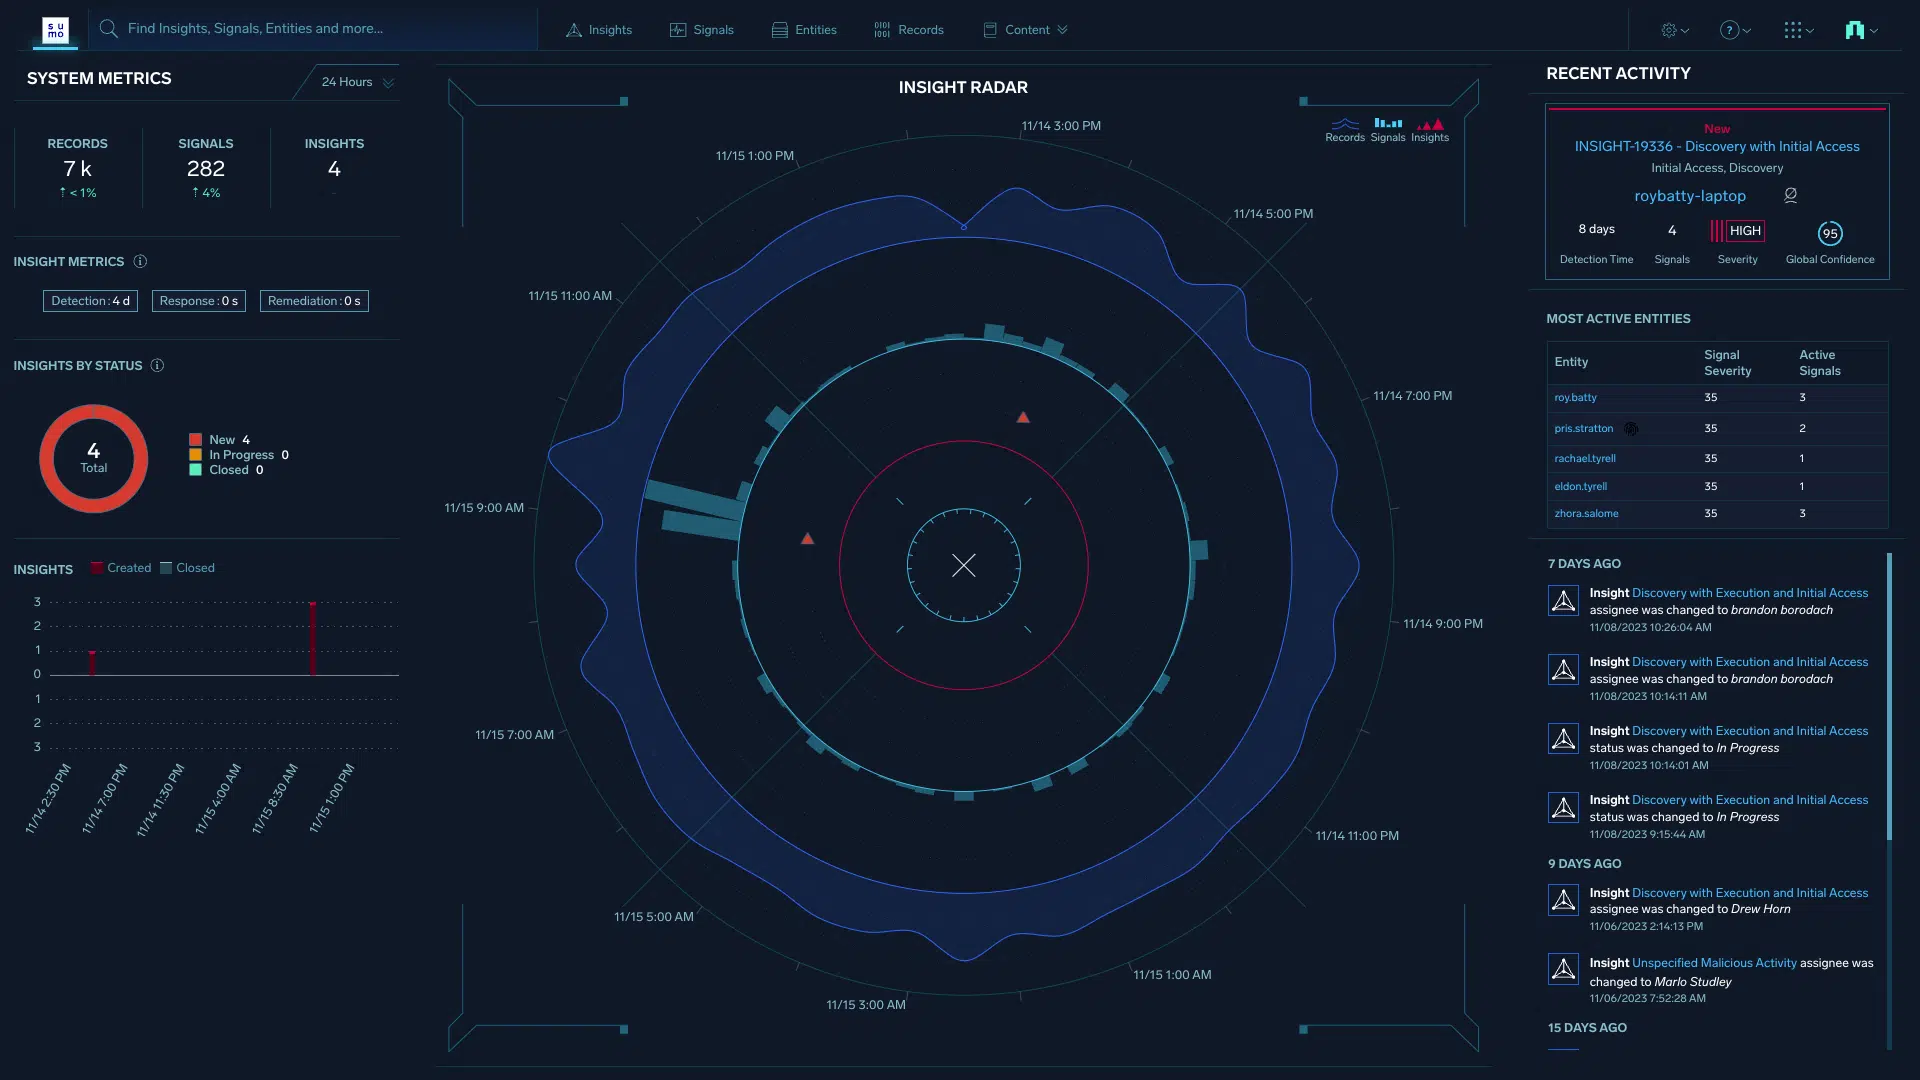
Cloud SIEM

SIEMソリューションの評価方法

sl

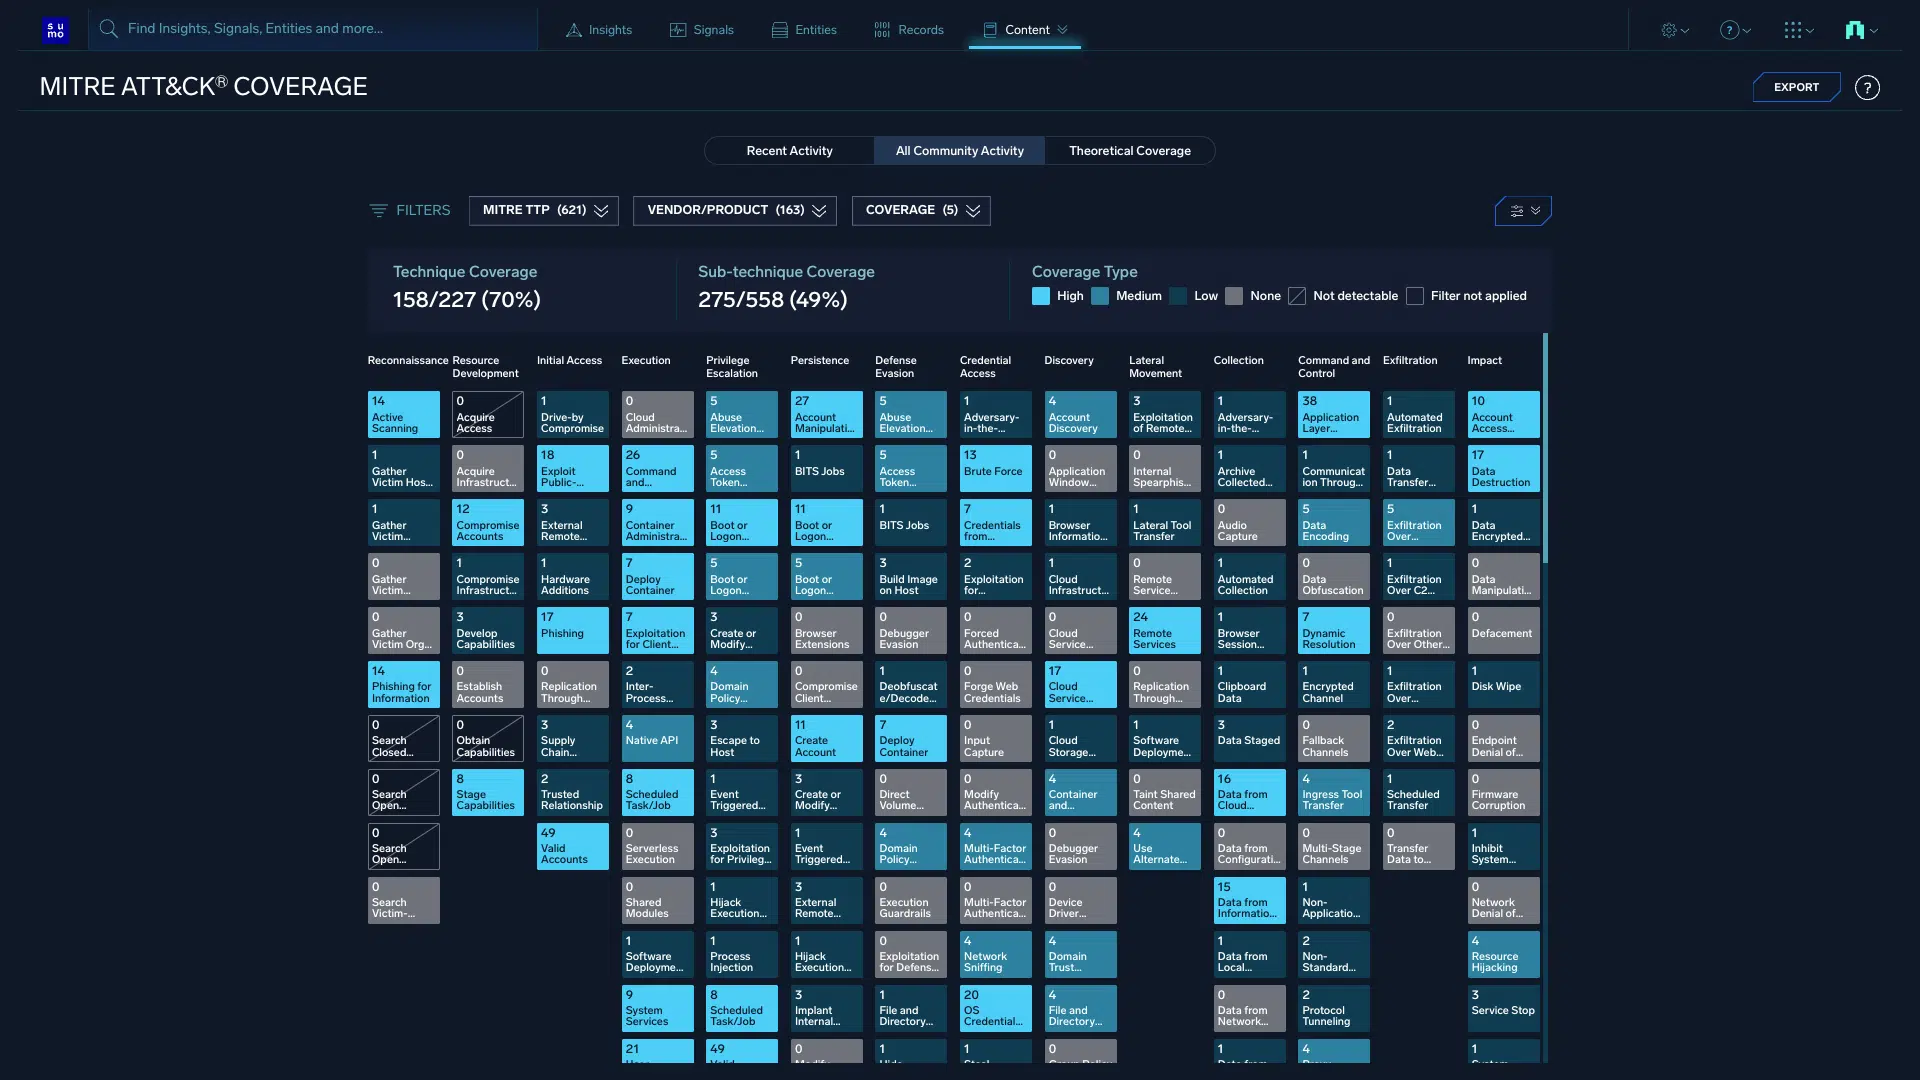
MITRE ATT&CKカバレッジエクスプローラー

sl

エージェントキルチェーンフレームワーク

sl whom9fenztg1

本格的なSOCを構築せずにクラウドワークロードを保護する方法

Jordan Andonov

Jordan Andonov

Security Engineer

“Managing multiple platforms and reviewing numerous dashboards became increasingly complex for our security team. From a security standpoint, we needed centralized collection and analysis that would make it easier and more efficient to keep track of everything in one place. ”
Maryna Veremenko

Maryna Veremenko

Engineering Manager
“Sumo Logic is really stable in handling our data volumes, and, most important, it empowers our engineers with the information they need. ”
“In particular, Sumo Logic’s powerful query functions serve as a competitive function, providing insightful results, like identifying similar errors or software versions with frequent issues. ”

Youngjip Kim, EVP, Head of AI Team

Farnoosh Azadi

Farnoosh Azadi

Director of Engineering
“Sumo Logic scrapes telemetry from more than 20,000 geographically distributed EC2 servers, thousands of Kubernetes pods, and a wide range of logs from a mix of other collection mechanisms. ”
Michael Basil

Michael Basil

Enterprise Systems Engineer, SRE

“With Sumo Logic, the quality of the product, it is just mega-powerful. The search and analytics engine is a huge draw. ”
“In particular, Sumo Logic’s powerful query functions serve as a competitive function, providing insightful results, like identifying similar errors or software versions with frequent issues. ”

Youngjip Kim, EVP, Head of AI Team

Maryna Veremenko

Maryna Veremenko

Engineering Manager

“Sumo Logic is really stable in handling our data volumes, and, most important, it empowers our engineers with the information they need. ”
Iwan Eising

Iwan Eising

Team Lead of Service Reliability Architecture

“Our approach resulted in a doubling of our log ingestion in 2021 at an ingestion cost increase of only 10%, saving us around $1 million. ”
Kal Patel

Kal Patel

VP, Platform Engineering

“With PagerDuty alerts tied to dashboards and playbooks, our team can move swiftly from alert to resolution. ”
Raj Desikavinayagompillai

Raj Desikavinayagompillai

US Cloud Operations Lead

“Every minute we waste is time which we can save to recover incidents quickly. ”
Sean Harley

Sean Harley

EVP & CIO

“Sumo Logic is at the heart of our DevSecOps strategy to bring security central to the application development functions and give us the data for our decision making. ”
Rick Jury

Rick Jury

Lead, Tools and Automation

“Over a 12 month period we tripled the size of our existing log analytics nodes and storage but our company’s phenomenal growth meant that we were still at peak load for this platform. The overloaded system negatively impacted users: log ingestion times were unpredictable, and search performance was poor. ”
Rajay Rai

Rajay Rai

CIO

“We have a unified approach with Sumo Logic that gives us central visibility into our observability, business intelligence and security monitoring needs. This means that we all work from the same data without multiple tools. ”
Alvin Lim

Alvin Lim

Head of Information Security
“Sumo Logic helps us accelerate impact by identifying impactful findings and showing us a clear path to investigation and remediation, all delivered through a streamlined, consolidated Cloud platform. ”
Mathias Faure

Mathias Faure

CTO, Standard Chartered
“We scan our code base hourly and log all the vulnerabilities that pop up. Then, we automatically create tickets for the teams to action. This process fosters great collaboration between our DevSecOps and DevOps teams. ”
“In particular, Sumo Logic’s powerful query functions serve as a competitive function, providing insightful results, like identifying similar errors or software versions with frequent issues. ”

Youngjip Kim, EVP, Head of AI Team

“From the beginning, the partnership from Sumo Logic has been great. They invested time to help us, and it was definitely an important element of our early success with the solution. ”

Chaitanya Pallapothula, SVP, Omni-Channel Technology
Scott Ashlock

Scott Ashlock

North America Security Operations Manager

“What set Sumo Logic apart from the rest was the speed at which we could search. It was incredible, and Sumo Logic beat out every other vendor by a large margin. ”
“Sumo Logic has helped us effectively manage our hybrid infrastructure and accelerate innovation. ”

Glenn Watt, CISO

Patrick Kolby

Patrick Kolby

Chief Security Officer

“AI-driven triage and plain-language summaries allow us to quickly understand what’s happening across multiple events and how they’re connected. ”
Biju Samuel

Biju Samuel

VP, IT and Operations

“Sumo Logic has given us the data insights needed to confidently serve the largest and most complex financial solutions. ”
“It has been easy, and almost completely hands-off to get Cloud SIEM Enterprise deployed and running. It’s been fairly easy for me to get log sources pointed at it, and the out-of-the-box content and rules helped tremendously. ”

Information Security, Operations Manager

Omar Koncobo

Omar Koncobo

IT Director of e-commerce/Digital and Marketing Systems

“Logs are like gold when you’re trying to troubleshoot an issue. So, make sure you have visibility into your logs to quickly see issues and address them to reduce your mean time to resolution. ”
“From the beginning, the partnership from Sumo Logic has been great. They invested time to help us, and it was definitely an important element of our early success with the solution. ”

Chaitanya Pallapothula, SVP, Omni-Channel Technology
Brandon Hewgill

Brandon Hewgill

Head of Information Security

“With powerful query functions coupled with intuitive AI integration and Mobot (the DojoAI at your side), nothing is impossible — plus the ability to automate the reduction of noise within the platform to allow for more streamlined insights where and when you need it. ”
Patrick Kolby

Patrick Kolby

Chief Security Officer
“AI-driven triage and plain-language summaries allow us to quickly understand what’s happening across multiple events and how they’re connected. ”
Dan Jackson

Dan Jackson

Principal Architect

“Sumo Logic has brought order, standards, and visibility to what had been a very haphazard approach to dealing with our massive amounts of machine data. ”
Hiroaki Kobayashi

Hiroaki Kobayashi

Sr Engineer, Infrastructure

“By linking the company’s internal authentication system, Sumo Logic can be used for centralized management of authorizations and rights. ”
Kal Patel

Kal Patel

VP, Platform Engineering

“With PagerDuty alerts tied to dashboards and playbooks, our team can move swiftly from alert to resolution. ”
Junichiro Baba

Junichiro Baba

Chief of Staff

“Sumo Logic has a simpler script for visualization than its competitors, making it easier to manage logs. The cost performance is also overwhelming. ”
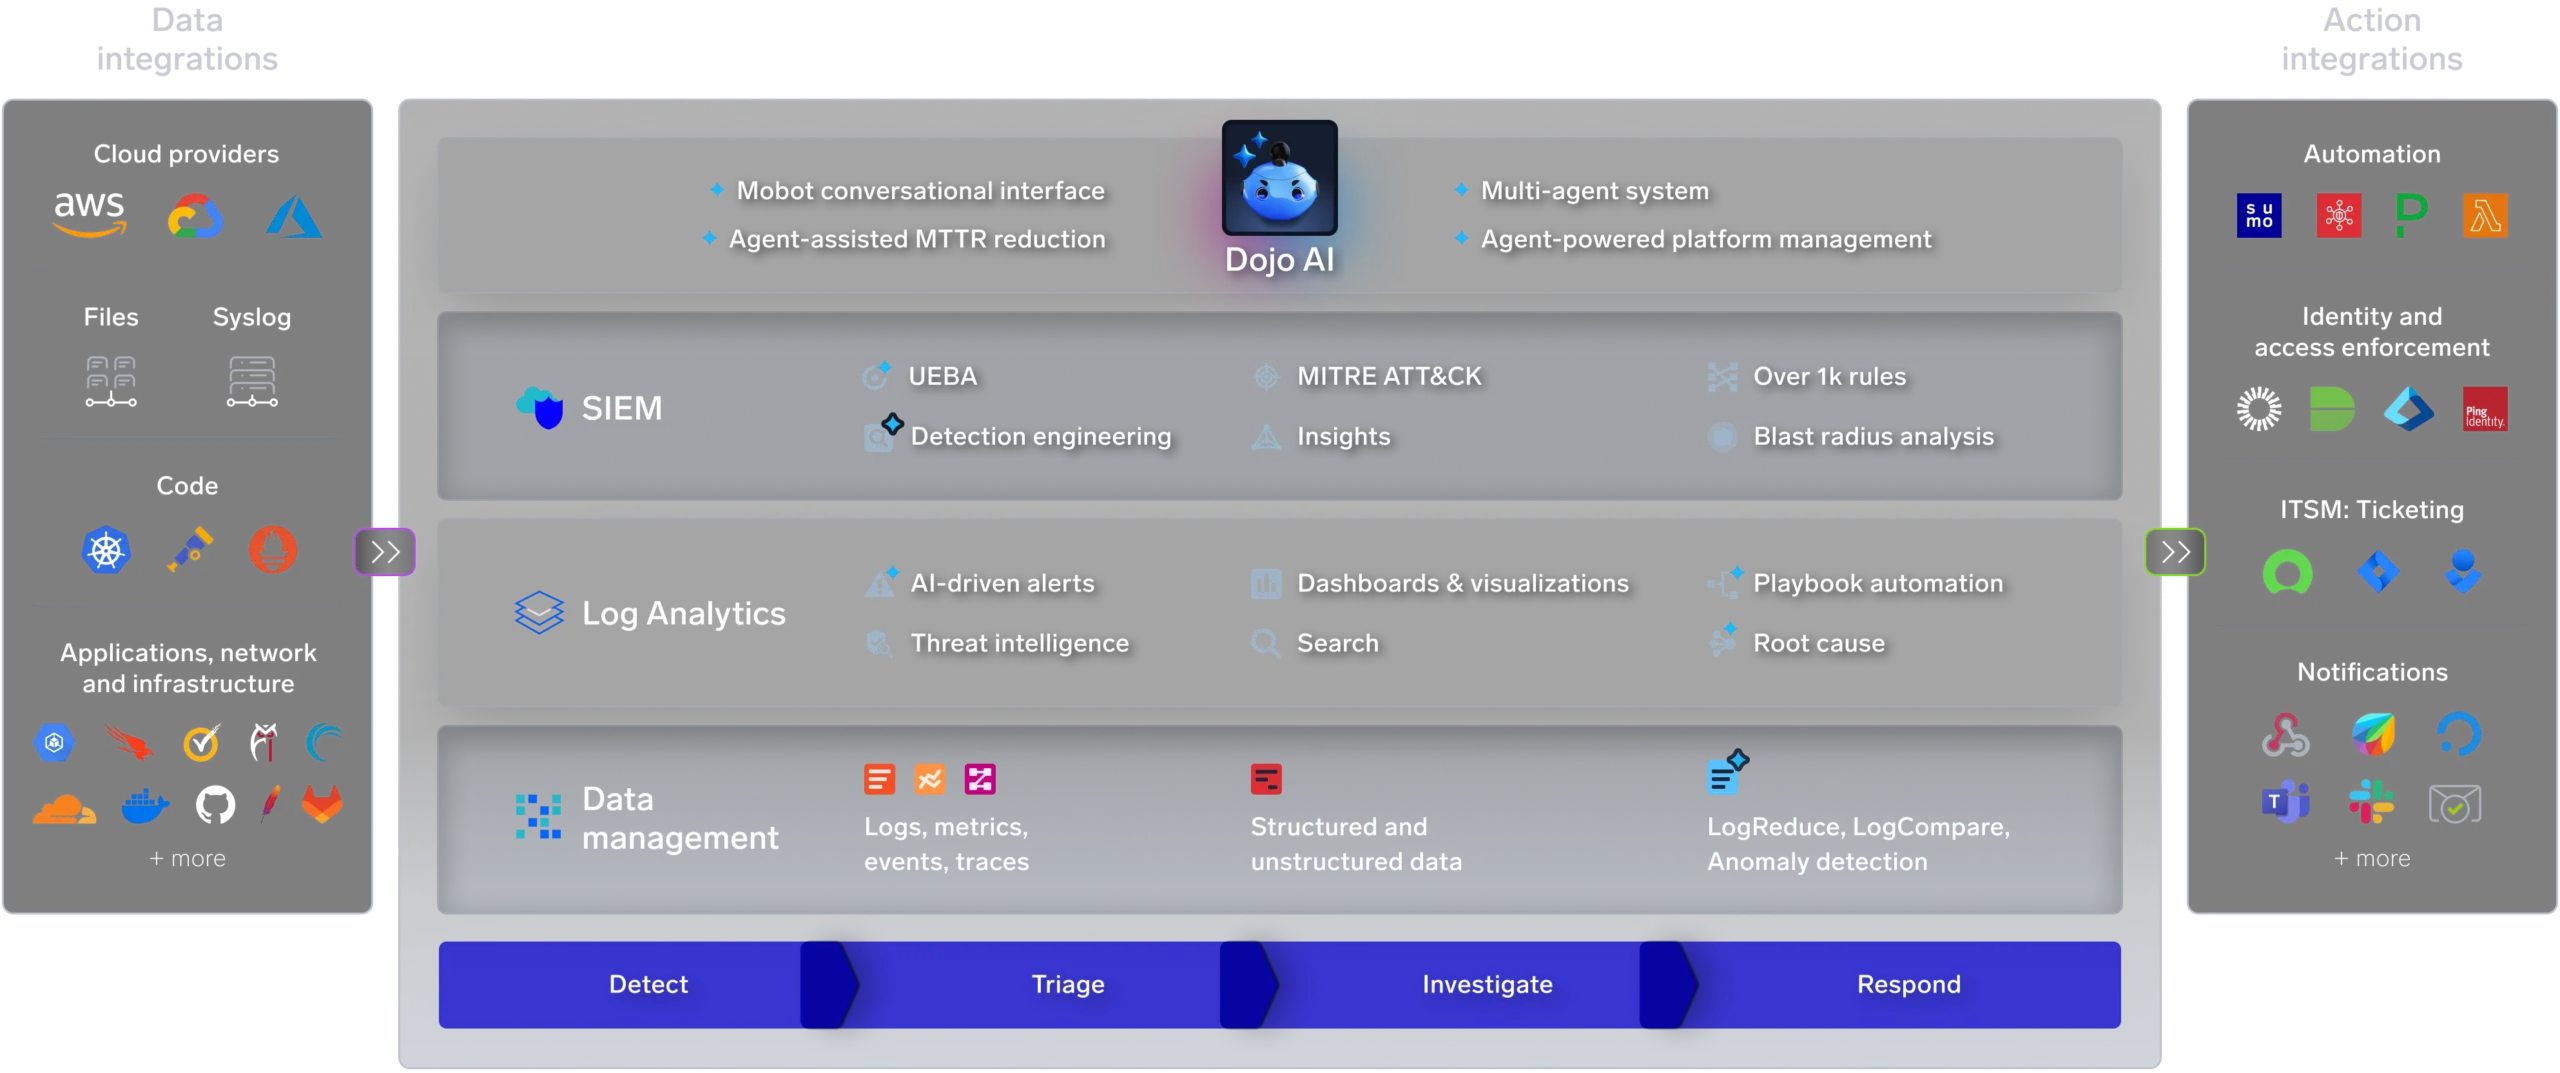
sumo logic dojo platform diagram clear@3x scaled

Sumo Logicを選ぶ理由

Sumo LogicのクラウドSIEM技術の利点

セキュリティオペレーションセンター(SOC)を構築。セキュリティ脅威の調査を1件あたり4時間短縮し、誤検知を90%削減。

Automated Insights

自動化されたインサイト

優先度付きアラートの向こう側。ユーザーとネットワークのコンテキストで強化された実用的な洞察により、脅威ハンティングを加速させます。

Cloud native architecture

クラウドネイティブのアーキテクチャ

必要に応じてスケーリングできます。当社のSIEMはマルチテナント対応のスケーラビリティと弾力性を提供し、セキュリティチームにSOCの効率化を実現します。

UebaBaseline

UEBAのベースライン作り

ユーザー行動をより迅速に学習し、誤検知を減らしたスマートな異常検知を実現します。

ThreatIntelligenceEnrichment

脅威インテリジェンスの強化

信頼できる複数の情報源(自社でキュレーションしたフィードを含む)からの脅威インテリジェンスが、各アラートを文脈化することで調査と対応を加速します。

Detection as code

ソフトウェアとしての検出

ソフトウェアのように検出ルールを管理し、GitHubと直接同期します。

Smarter Analyst

よりスマートなアナリスト体験

ログ、検知、自動化を横断して、一貫した体験で作業できます。

SIEMソフトウェアは、セキュリティ情報管理 (SIM) ツールとセキュリティイベント管理 (SEM) ツールの機能を統合したものです。

SIMテクノロジーは、さまざまなデータタイプで構成されるログから情報を収集します。対照的に、SEMは特定の種類のイベントをより詳しく調べます。

複数のソースから収集されるコンピューターログデータを一元化しながら、自動生成されたコンピューターログからセキュリティ関連のデータを収集、監視、分析することができます。この包括的なセキュリティ ソリューションにより、正式なインシデント対応プロセスが可能になります。

SIEMソフトウェアツールの代表的な機能は以下のとおりです。

  • セキュリティ関連データの収集、分析、および提示
  • セキュリティアラートのリアルタイム分析
  • セキュリティデータのロギングとレポートの生成
  • アイデンティティおよびアクセス管理
  • ログ監査とレビュー
  • インシデント対応とセキュリティ運用

もっと詳しく

SIEM は、以下を含む主要な機能を通じて、優れたインシデント対応とエンタープライズセキュリティの成果を実現します:

データ収集 – SIEM ツールは、さまざまなソースやアプリケーションからのイベントログやシステムログ、セキュリティデータを 1 か所に集約します。

相互関連付け – SIEM ツールは、共通属性を持つデータ断片を結び付ける多様な相互関連付けテクノロジーを活用し、そのデータを SecOps チームが活用可能な情報へと変換するのをサポートします。

アラート – SIEM ツールは、セキュリティイベントを示す可能性のある事前定義済みのシグナルやパターンが検出された場合に、SecOps チームや IT チームに自動的にアラートを発するように構成できます。

データの保持 – SIEM ツールは大量のログデータを保存するように設計されているため、セキュリティチームは一定期間のデータを相互に関連付けることができ、当初検出されなかった可能性のある脅威やサイバー攻撃についてフォレンジック調査を行うことができます。

解析、ログの正規化と分類 – SIEM ツールは、数週間あるいは数か月前に生成された可能性のあるログの解析を容易にします。解析、ログの正規化、分類は、SIEM ツールの追加機能であり、ログの検索性を高め、数百万件ものログエントリを精査する場合でもフォレンジック分析を可能にします。

SIEM の代表的なユースケースを以下に紹介します:

コンプライアンス – データセキュリティおよびプライバシーコンプライアンス規制を満たすため、コンプライアンスプロセスを合理化。例えば、顧客からクレジットカード情報を収集する加盟店向けのデータセキュリティ基準であるPCI DSSに準拠するため、SIEMはネットワークアクセスとデータベース内のトランザクションログを監視し、顧客データへの不正アクセスがないことを確認します。

インシデント対応 – インシデント対応活動の効率性と迅速性を向上。侵害が検出された場合、SecOpsチームはSIEMソフトウェアを使用して、攻撃が企業セキュリティシステムをどのように突破したか、また侵害の影響を受けたホストやアプリケーションを迅速に特定できます。SIEMツールは自動化されたメカニズムを通じて、こうした攻撃に対処することさえ可能です。

脆弱性管理 – ネットワークとITインフラを積極的にテストし、サイバー攻撃の侵入経路を検知・対処。SIEMソフトウェアツールは、ネットワーク脆弱性テスト、スタッフ報告、ベンダー発表と並んで、新たな脆弱性を発見するための重要なデータソースなのです。

脅威インテリジェンス – 高度な持続的脅威(APT)やゼロデイ脅威に対する脆弱性を低減するため、緊密に連携。SIEMソフトウェアツールは、アプリケーションスタック内で生成されるログデータを収集・分析するためのフレームワークを提供します。UEBA を活用すれば、内部脅威をプロアクティブに発見できます。

Sumo Logic SIEMは、Sumo Logicセキュリティプラットフォームの一部であり、ログを活用したクラウドネイティブなマルチユース型ソリューションです。SIEMに加えて、Sumo Logicの堅牢なログ分析プラットフォームは、インフラストラクチャ監視、アプリケーションオブザーバビリティ、セキュリティ用ログをサポートし、アプリの監視、トラブルシューティング、セキュリティ確保を実現します。

お客様がSumo Logic SIEMを選ぶ理由は、以下の差別化された機能にあります。

統合されたログ分析プラットフォーム – 開発、セキュリティ、運用、基幹業務チーム向けの単一統合ソリューション。

クラウドネイティブな分散アーキテクチャ – ログを活用したスケーラブルなマルチテナントプラットフォームで、データの損失は一切ありません。

階層化されたアナリティクスとクレジットライセンス – データ増加に予算の増加が追いつかない場合でも、スケーリング可能な柔軟なサブスクリプションをお楽しみいただけます。

機械学習と高度なアナリティクス – 機械学習を活用して、問題をより迅速に特定、調査、解決します。

すぐに使える監査とコンプライアンス – 最も広範な認証と証明に対するコンプライアンスを簡単に実証できます。

セキュリティバイデザイン – 当社は認証、証明、ペネトレーションテスト、コードレビュー、有償バグバウンティプログラムに毎年数百万ドルを投資しています。