위협으로 업무가 중단되기 전에 차단하세요.

전 세계 2,500개 이상의 고객사가 신뢰합니다.

Alaska Airlines logo
Dolby logo
Grammarly logo
Hello Fresh logo
Samsung logo
Ulta Beauty logo

AI SOC vs. white box AI

모든 것을 자율적으로 처리하겠다고 약속하는 “AI SOC” 스타트업들이 점점 더 늘어나고 있습니다. 이들은 경고를 분류하고, 위협을 조사하며, 심지어 플레이북까지 실행합니다. 버튼 하나만 누르면 기계가 알아서 일을 처리해 주고, 마법 같은 순간을 즐길 수 있습니다.

sl n4iietdfjfgt
sl n4iietdfjfgt
Cloud SIEM

SIEM 솔루션 평가 방법

sl

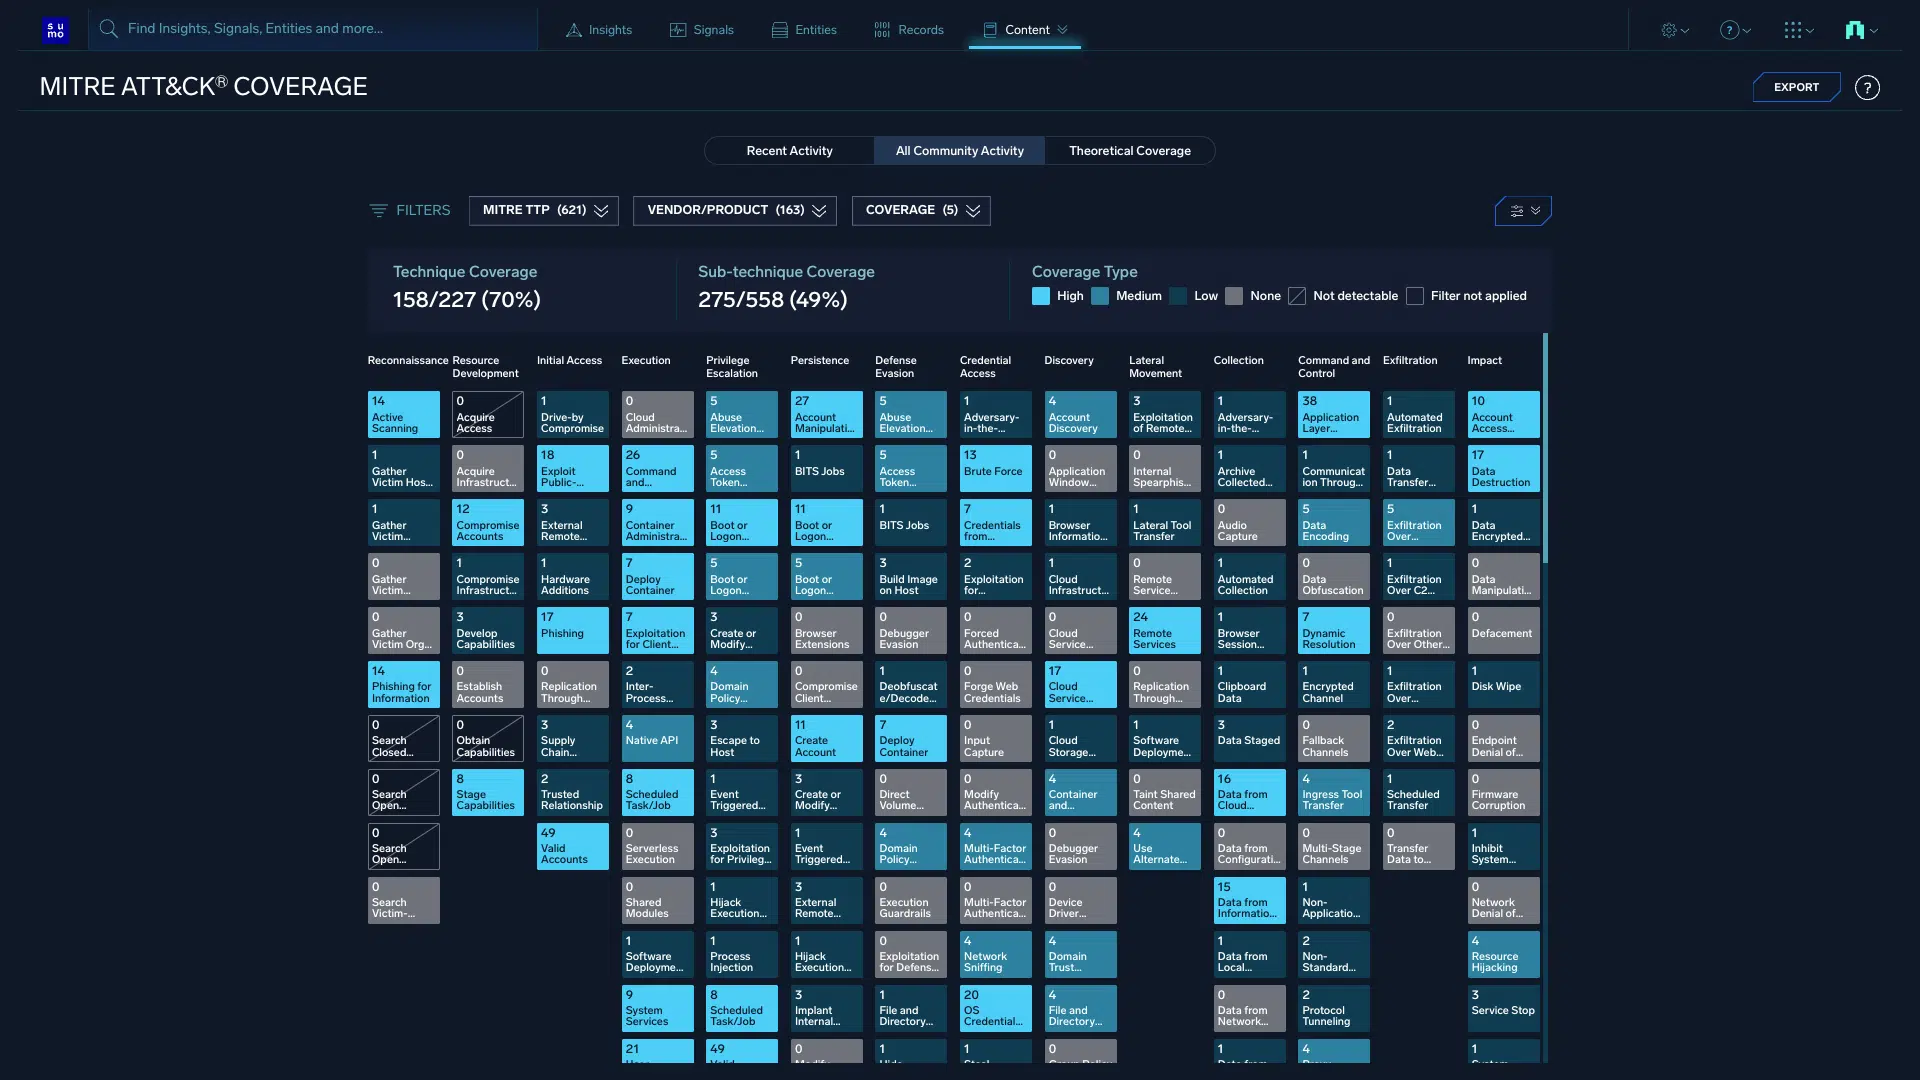
MITRE ATT&CK 커버리지 탐색기

sl

에이전트 킬 체인 프레임워크

sl whom9fenztg1

전체 규모의 SOC를 구축하지 않고 클라우드 워크로드를 보호하는 방법

Jordan Andonov

Jordan Andonov

Security Engineer

“Managing multiple platforms and reviewing numerous dashboards became increasingly complex for our security team. From a security standpoint, we needed centralized collection and analysis that would make it easier and more efficient to keep track of everything in one place. ”
Maryna Veremenko

Maryna Veremenko

Engineering Manager
“Sumo Logic is really stable in handling our data volumes, and, most important, it empowers our engineers with the information they need. ”
“In particular, Sumo Logic’s powerful query functions serve as a competitive function, providing insightful results, like identifying similar errors or software versions with frequent issues. ”

Youngjip Kim, EVP, Head of AI Team

Farnoosh Azadi

Farnoosh Azadi

Director of Engineering
“Sumo Logic scrapes telemetry from more than 20,000 geographically distributed EC2 servers, thousands of Kubernetes pods, and a wide range of logs from a mix of other collection mechanisms. ”
Michael Basil

Michael Basil

Enterprise Systems Engineer, SRE

“With Sumo Logic, the quality of the product, it is just mega-powerful. The search and analytics engine is a huge draw. ”
“In particular, Sumo Logic’s powerful query functions serve as a competitive function, providing insightful results, like identifying similar errors or software versions with frequent issues. ”

Youngjip Kim, EVP, Head of AI Team

Maryna Veremenko

Maryna Veremenko

Engineering Manager

“Sumo Logic is really stable in handling our data volumes, and, most important, it empowers our engineers with the information they need. ”
Iwan Eising

Iwan Eising

Team Lead of Service Reliability Architecture

“Our approach resulted in a doubling of our log ingestion in 2021 at an ingestion cost increase of only 10%, saving us around $1 million. ”
Kal Patel

Kal Patel

VP, Platform Engineering

“With PagerDuty alerts tied to dashboards and playbooks, our team can move swiftly from alert to resolution. ”
Raj Desikavinayagompillai

Raj Desikavinayagompillai

US Cloud Operations Lead

“Every minute we waste is time which we can save to recover incidents quickly. ”
Sean Harley

Sean Harley

EVP & CIO

“Sumo Logic is at the heart of our DevSecOps strategy to bring security central to the application development functions and give us the data for our decision making. ”
Rick Jury

Rick Jury

Lead, Tools and Automation

“Over a 12 month period we tripled the size of our existing log analytics nodes and storage but our company’s phenomenal growth meant that we were still at peak load for this platform. The overloaded system negatively impacted users: log ingestion times were unpredictable, and search performance was poor. ”
Rajay Rai

Rajay Rai

CIO

“We have a unified approach with Sumo Logic that gives us central visibility into our observability, business intelligence and security monitoring needs. This means that we all work from the same data without multiple tools. ”
Alvin Lim

Alvin Lim

Head of Information Security
“Sumo Logic helps us accelerate impact by identifying impactful findings and showing us a clear path to investigation and remediation, all delivered through a streamlined, consolidated Cloud platform. ”
Mathias Faure

Mathias Faure

CTO, Standard Chartered
“We scan our code base hourly and log all the vulnerabilities that pop up. Then, we automatically create tickets for the teams to action. This process fosters great collaboration between our DevSecOps and DevOps teams. ”
“In particular, Sumo Logic’s powerful query functions serve as a competitive function, providing insightful results, like identifying similar errors or software versions with frequent issues. ”

Youngjip Kim, EVP, Head of AI Team

“From the beginning, the partnership from Sumo Logic has been great. They invested time to help us, and it was definitely an important element of our early success with the solution. ”

Chaitanya Pallapothula, SVP, Omni-Channel Technology
Scott Ashlock

Scott Ashlock

North America Security Operations Manager

“What set Sumo Logic apart from the rest was the speed at which we could search. It was incredible, and Sumo Logic beat out every other vendor by a large margin. ”
“Sumo Logic has helped us effectively manage our hybrid infrastructure and accelerate innovation. ”

Glenn Watt, CISO

Patrick Kolby

Patrick Kolby

Chief Security Officer

“AI-driven triage and plain-language summaries allow us to quickly understand what’s happening across multiple events and how they’re connected. ”
Biju Samuel

Biju Samuel

VP, IT and Operations

“Sumo Logic has given us the data insights needed to confidently serve the largest and most complex financial solutions. ”
“It has been easy, and almost completely hands-off to get Cloud SIEM Enterprise deployed and running. It’s been fairly easy for me to get log sources pointed at it, and the out-of-the-box content and rules helped tremendously. ”

Information Security, Operations Manager

Omar Koncobo

Omar Koncobo

IT Director of e-commerce/Digital and Marketing Systems

“Logs are like gold when you’re trying to troubleshoot an issue. So, make sure you have visibility into your logs to quickly see issues and address them to reduce your mean time to resolution. ”
“From the beginning, the partnership from Sumo Logic has been great. They invested time to help us, and it was definitely an important element of our early success with the solution. ”

Chaitanya Pallapothula, SVP, Omni-Channel Technology
Brandon Hewgill

Brandon Hewgill

Head of Information Security

“With powerful query functions coupled with intuitive AI integration and Mobot (the DojoAI at your side), nothing is impossible — plus the ability to automate the reduction of noise within the platform to allow for more streamlined insights where and when you need it. ”
Patrick Kolby

Patrick Kolby

Chief Security Officer
“AI-driven triage and plain-language summaries allow us to quickly understand what’s happening across multiple events and how they’re connected. ”
Dan Jackson

Dan Jackson

Principal Architect

“Sumo Logic has brought order, standards, and visibility to what had been a very haphazard approach to dealing with our massive amounts of machine data. ”
Hiroaki Kobayashi

Hiroaki Kobayashi

Sr Engineer, Infrastructure

“By linking the company’s internal authentication system, Sumo Logic can be used for centralized management of authorizations and rights. ”
Kal Patel

Kal Patel

VP, Platform Engineering

“With PagerDuty alerts tied to dashboards and playbooks, our team can move swiftly from alert to resolution. ”
Junichiro Baba

Junichiro Baba

Chief of Staff

“Sumo Logic has a simpler script for visualization than its competitors, making it easier to manage logs. The cost performance is also overwhelming. ”
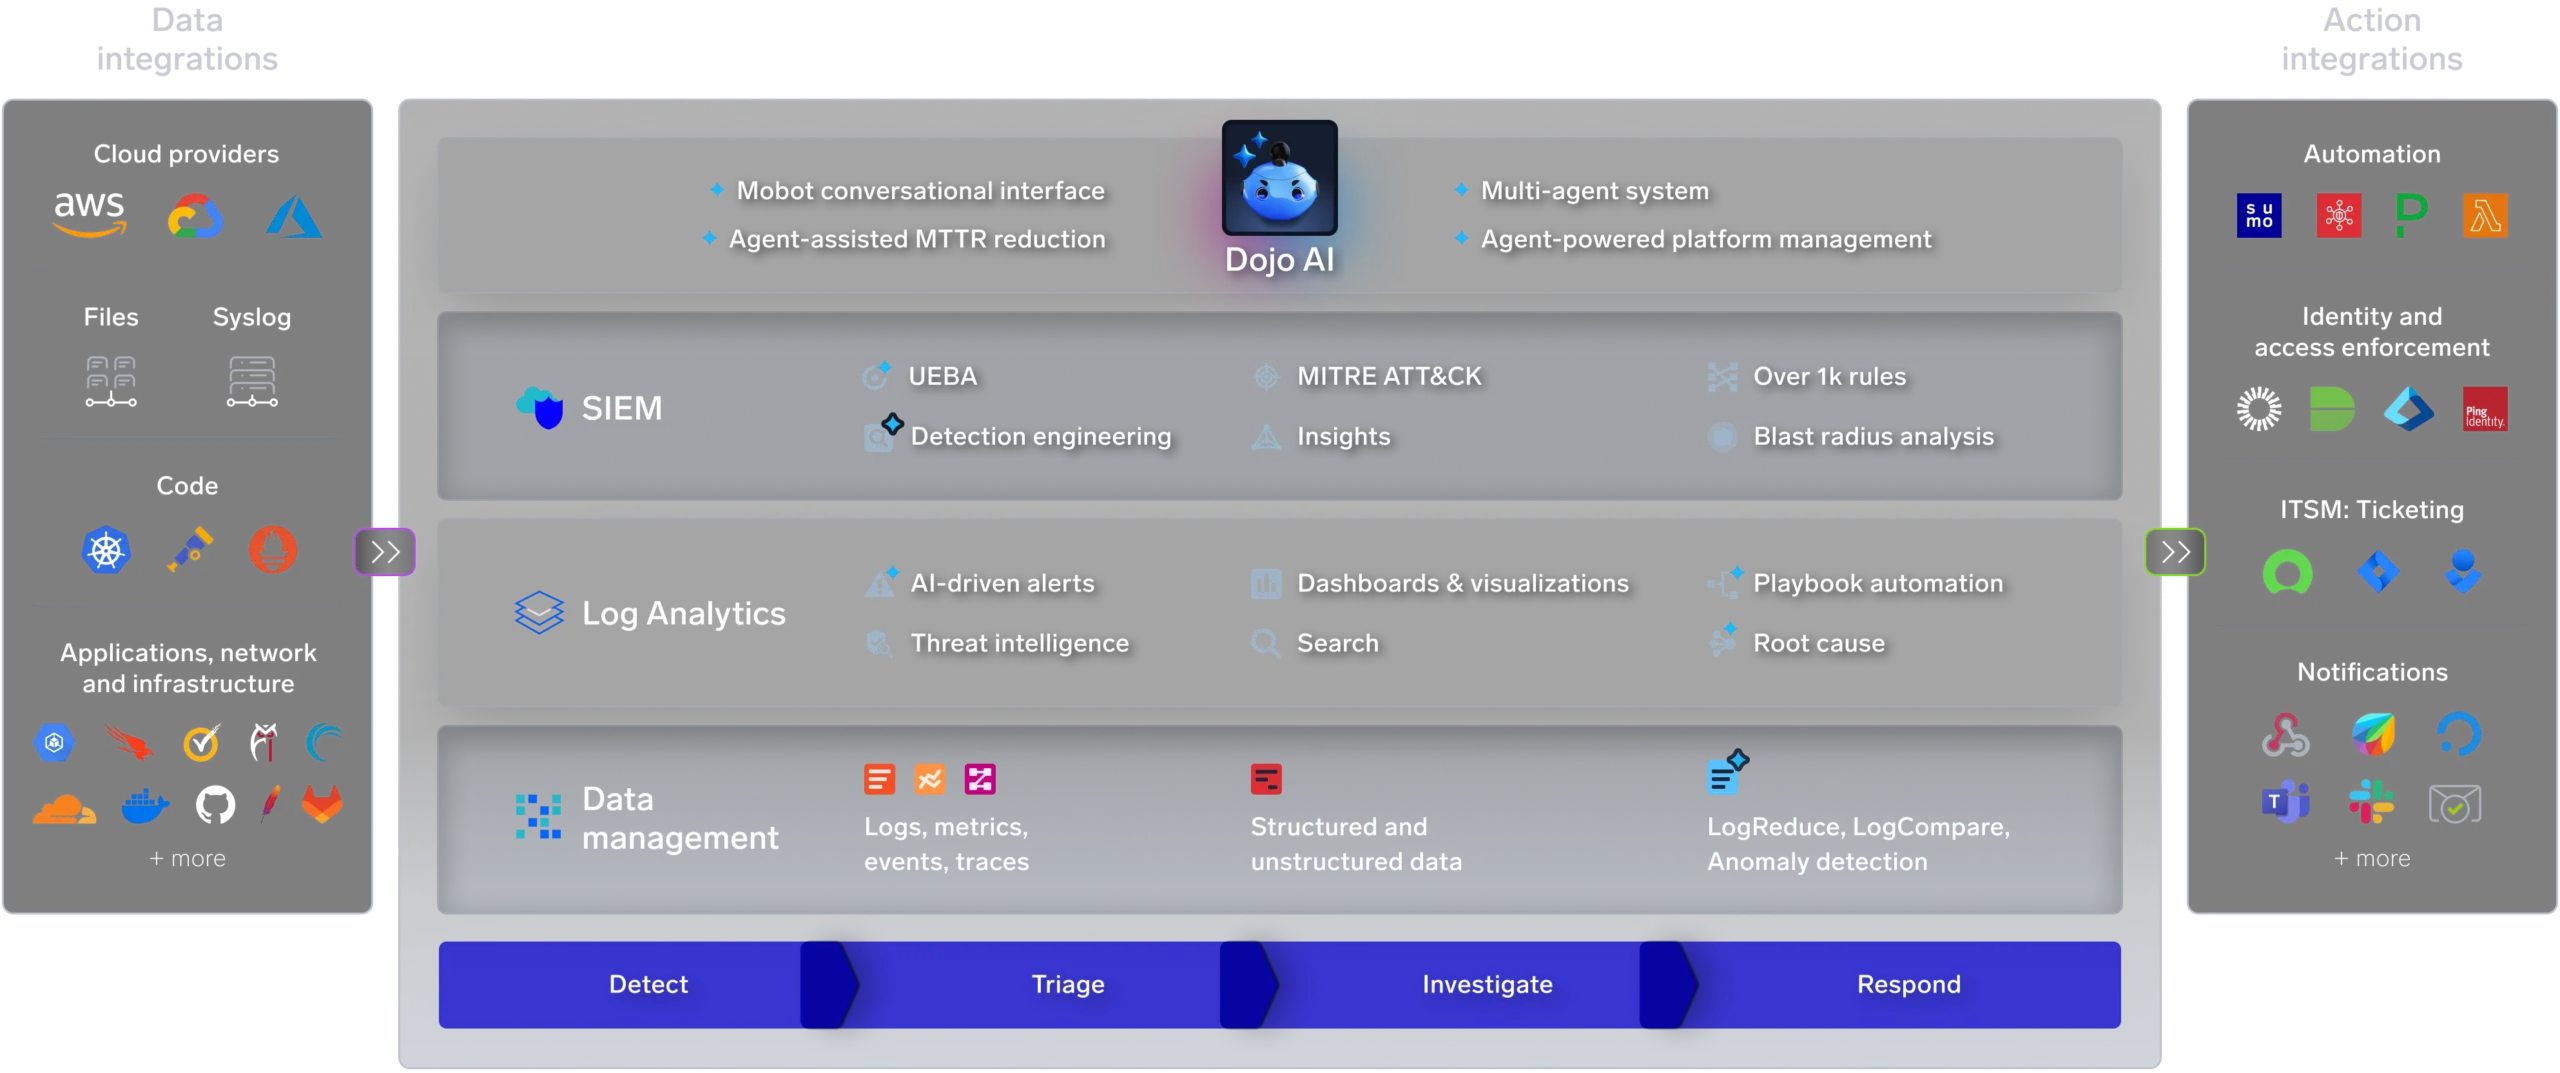
sumo logic dojo platform diagram clear@3x scaled

Sumo Logic을 선택해야 하는 이유

Sumo Logic 클라우드 SIEM 기술의 장점

보안 운영 센터(SOC)를 구축하세요. 보안 위협 조사당 4시간 절약, 오탐률 90% 감소.

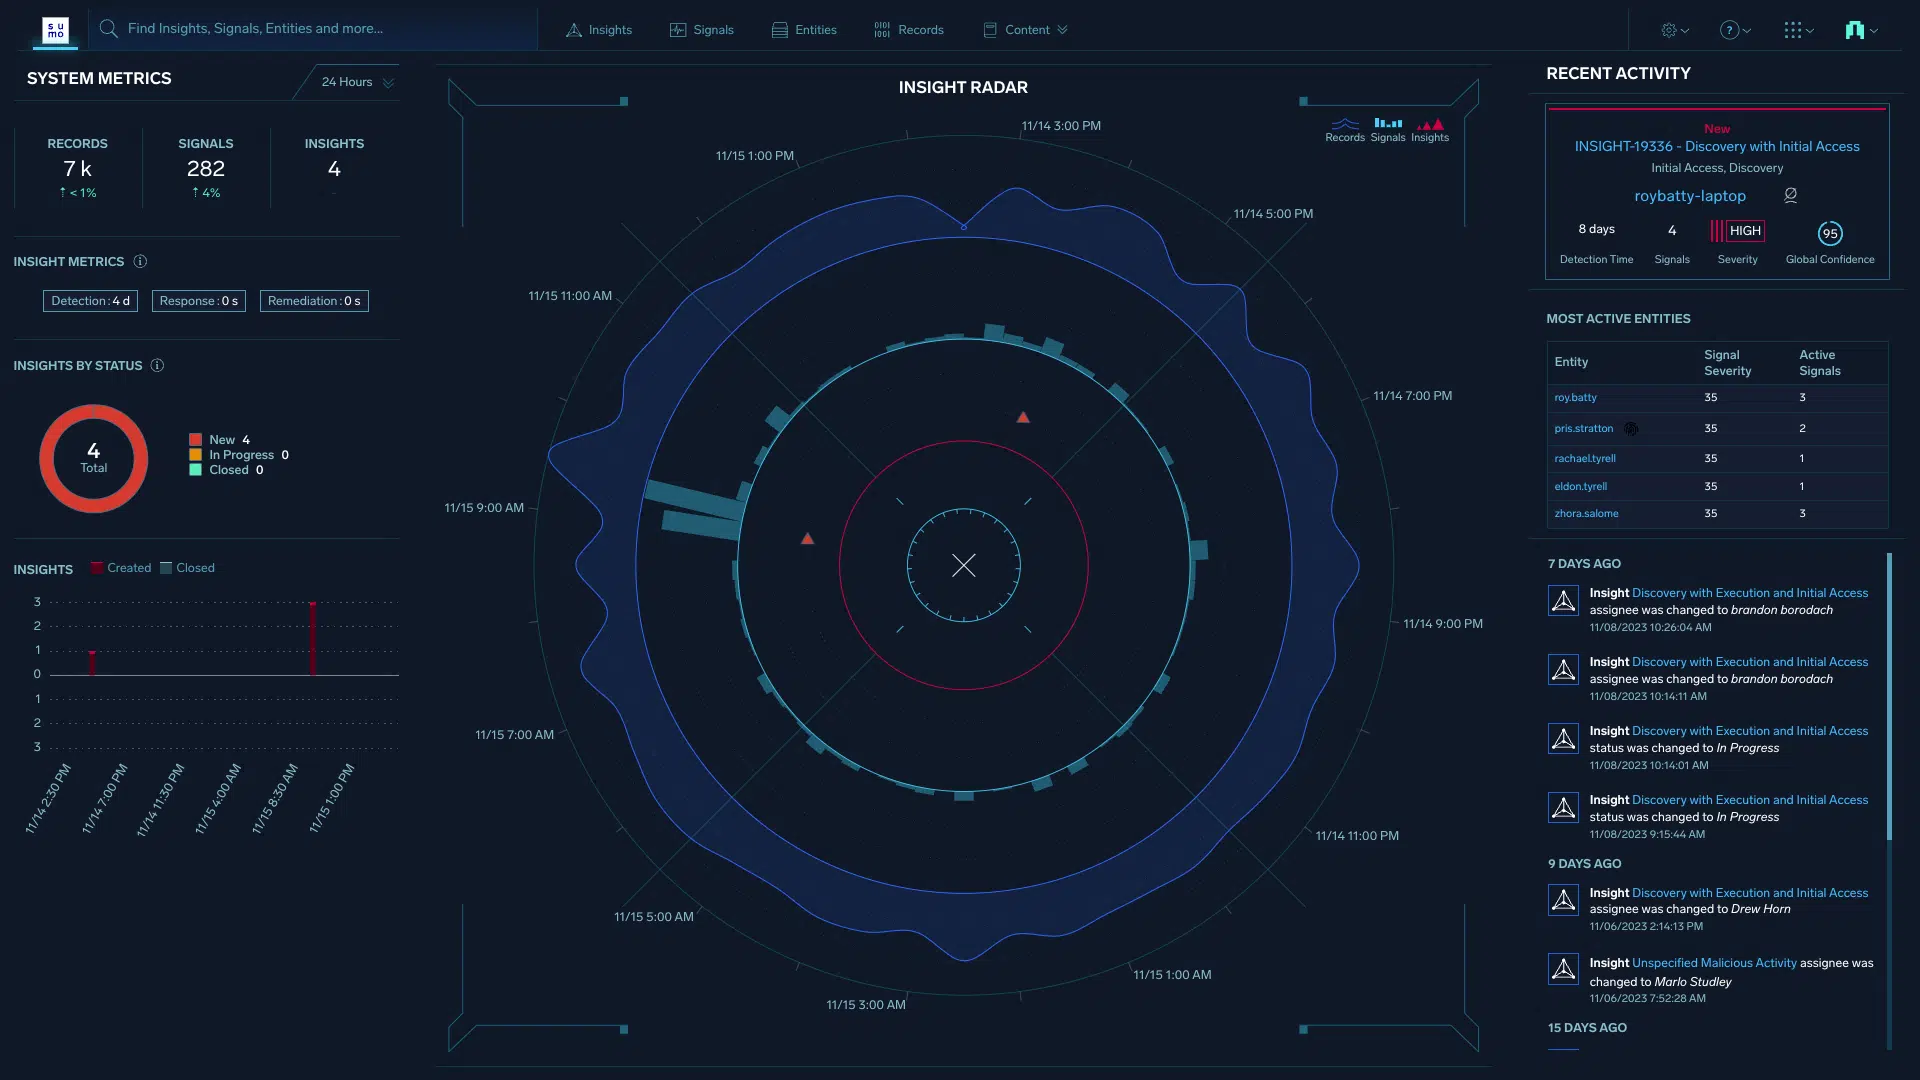
Automated Insights

인사이트 자동화

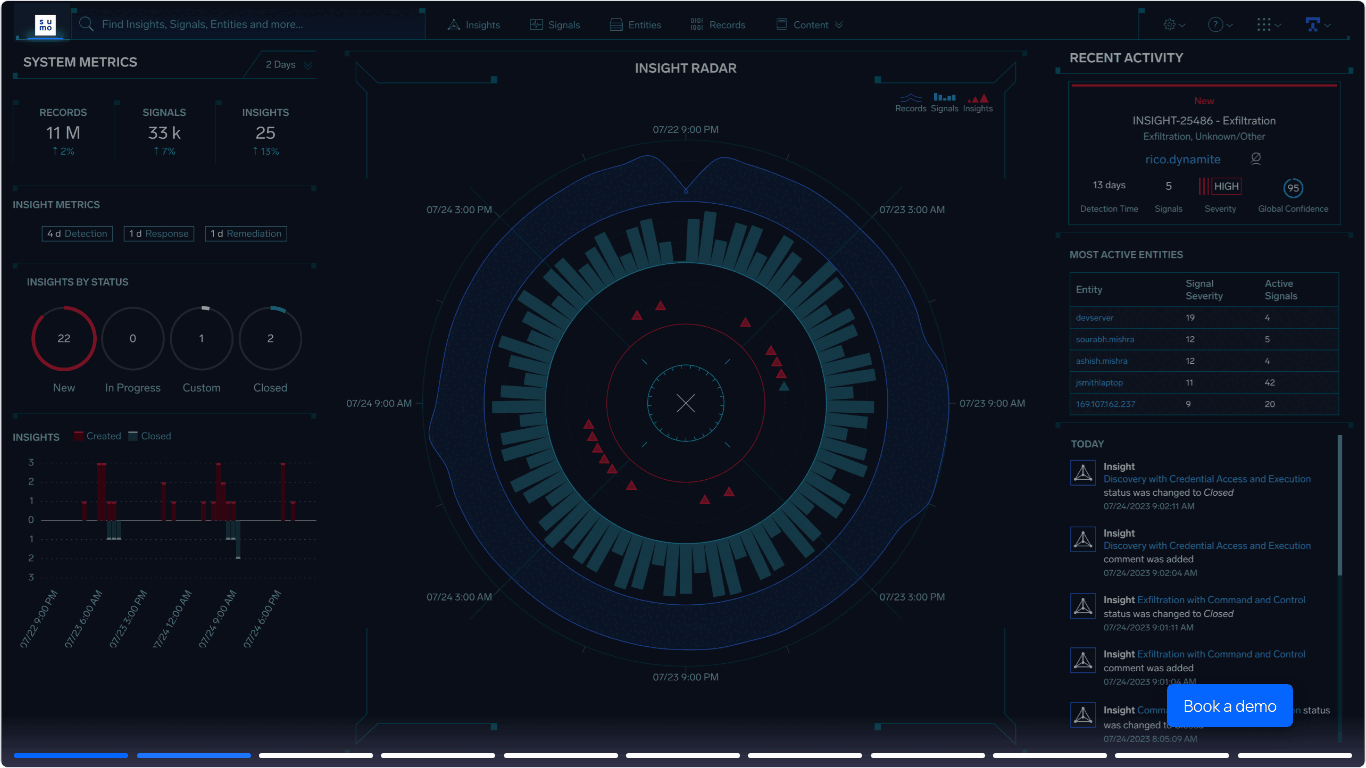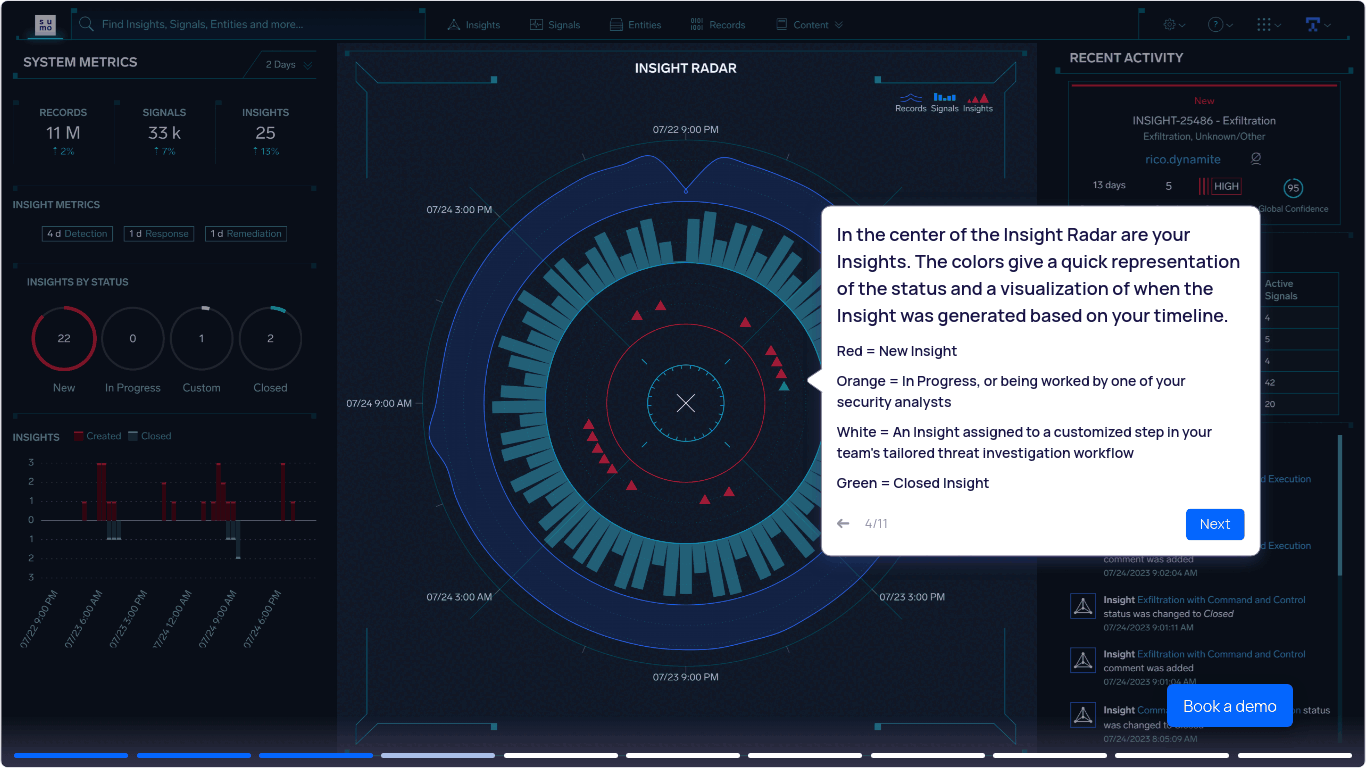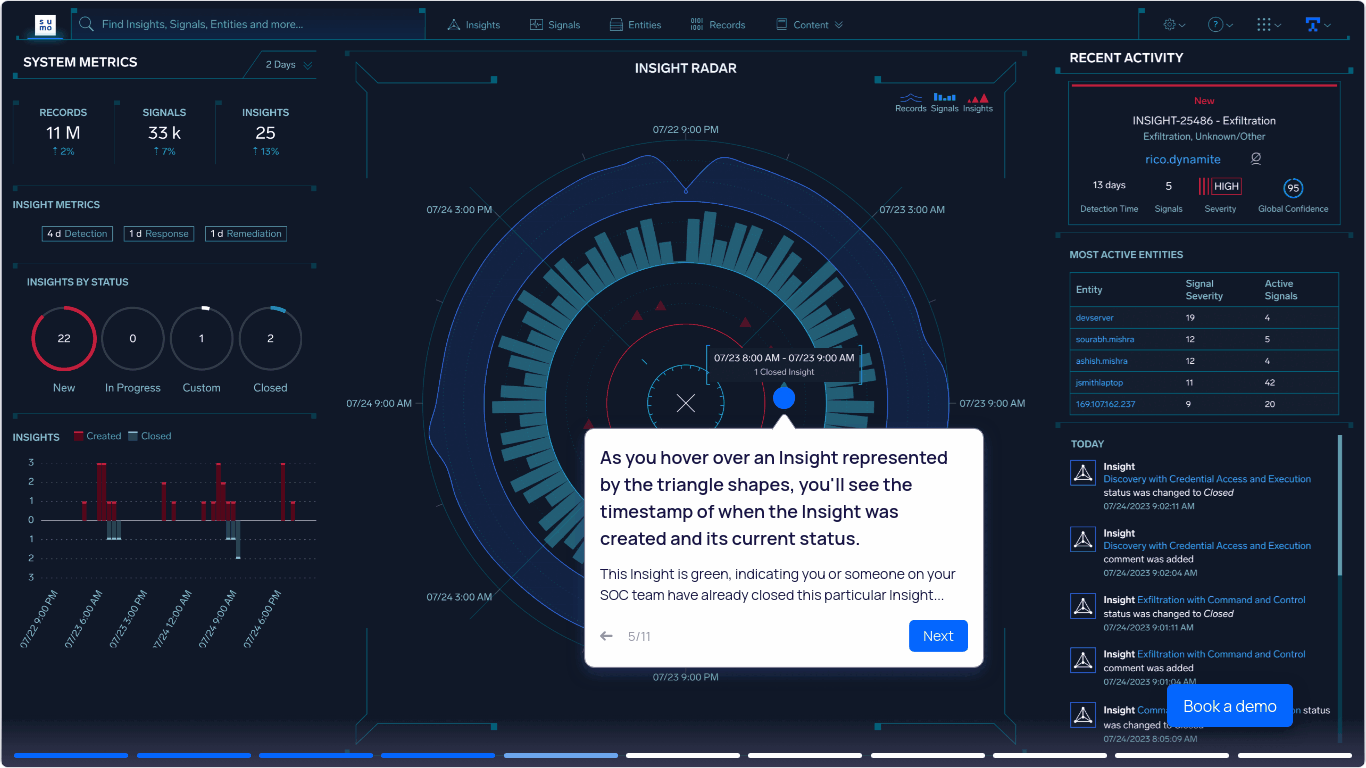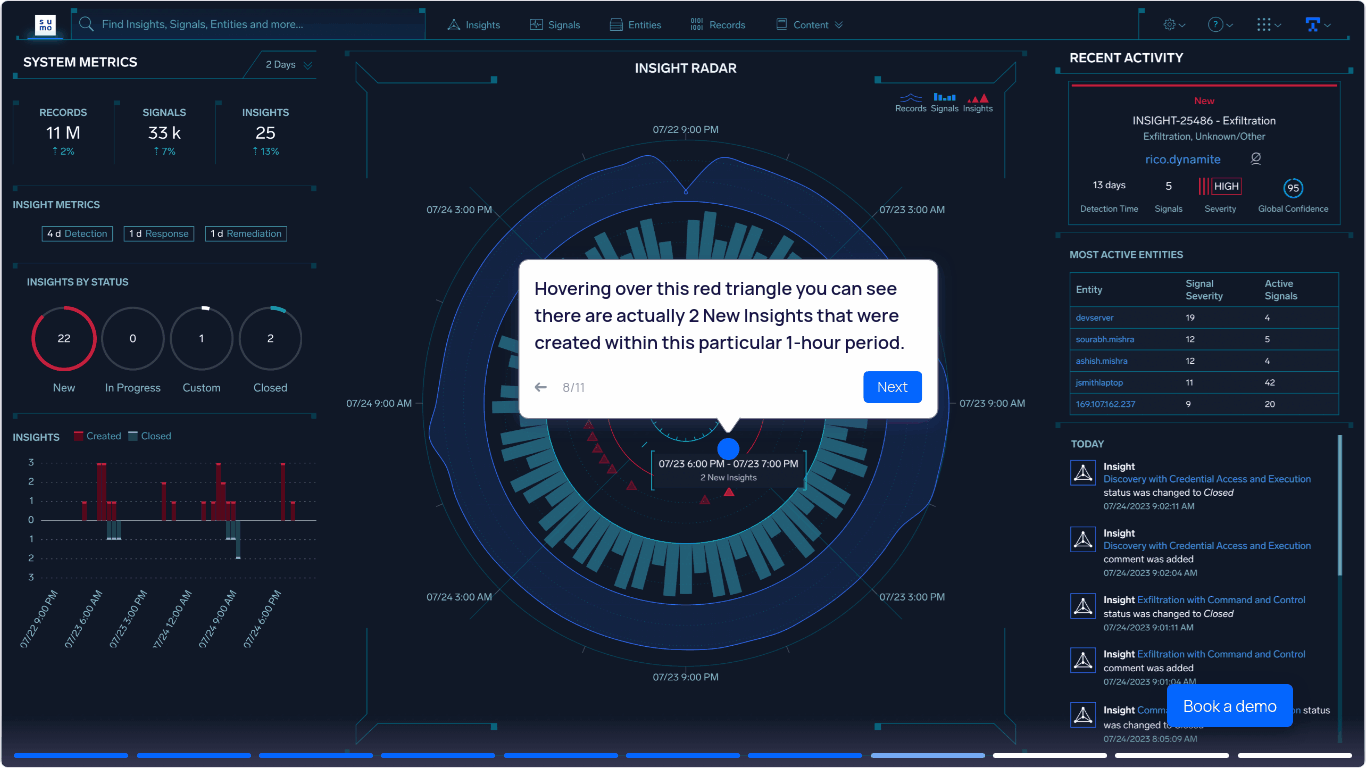
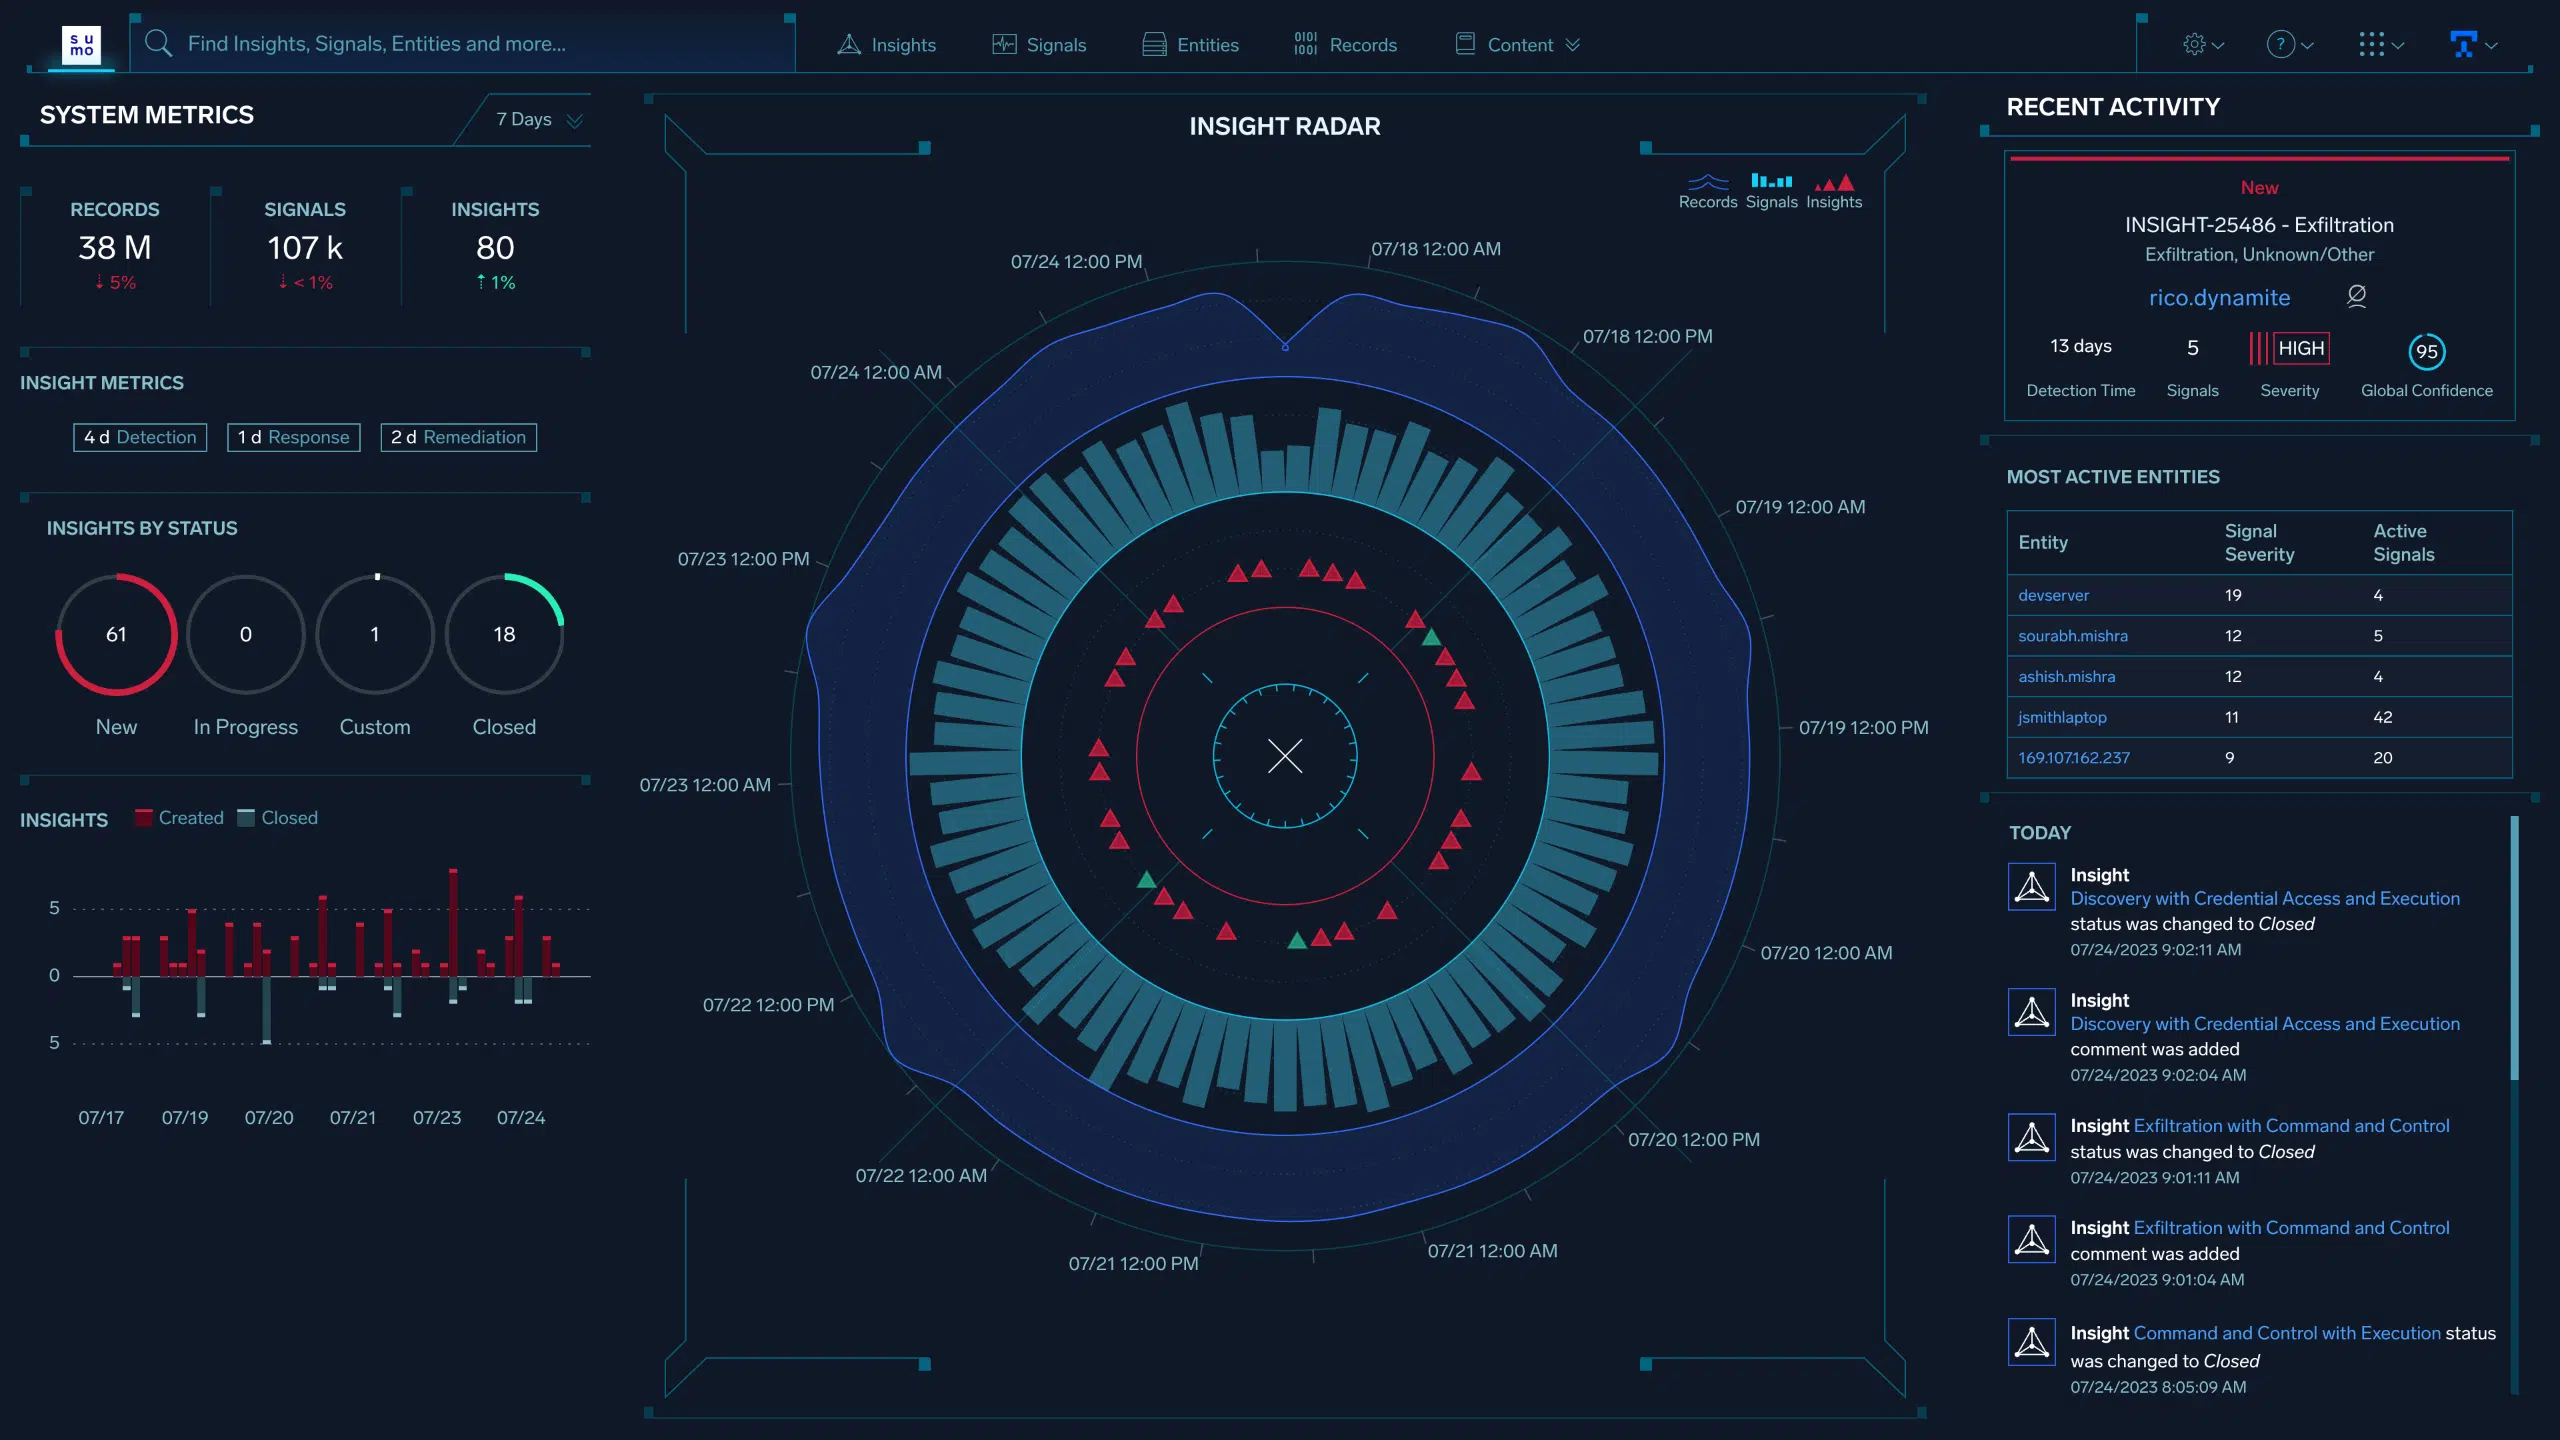
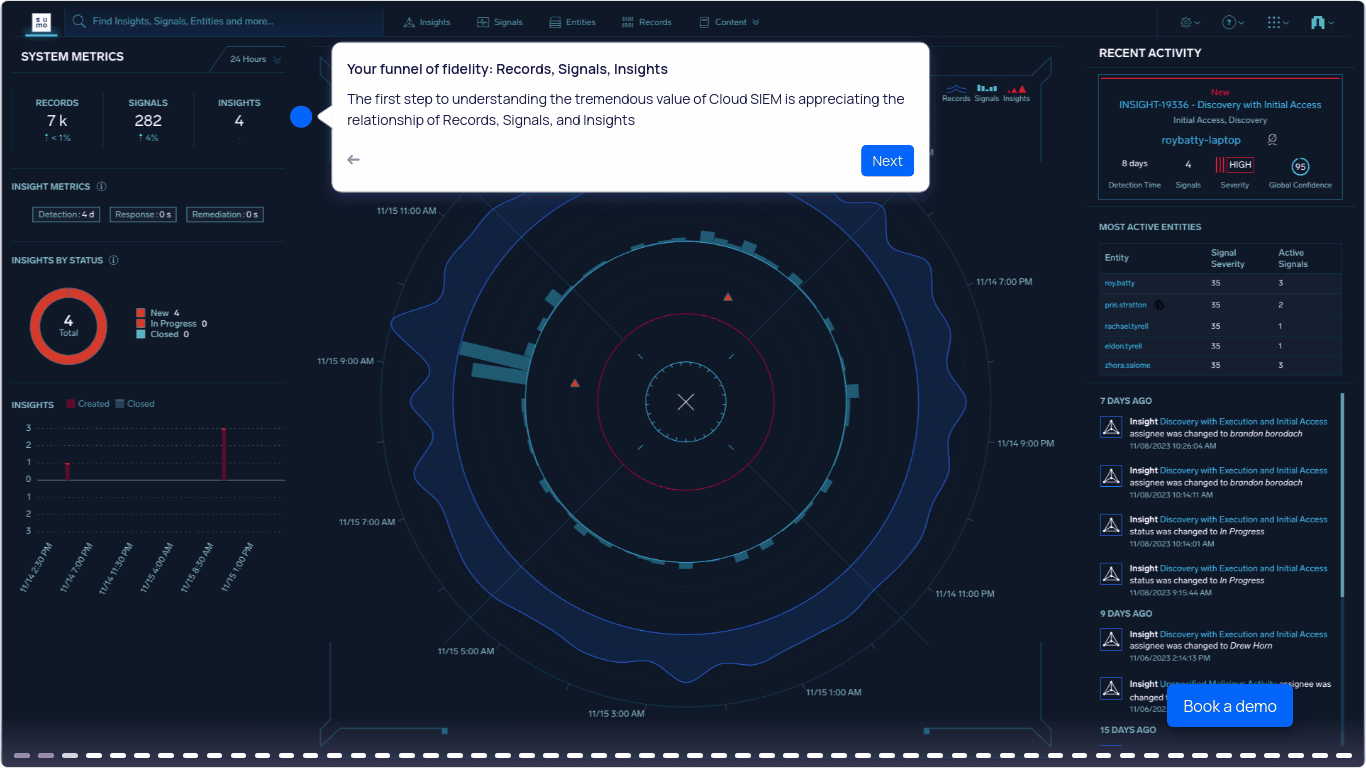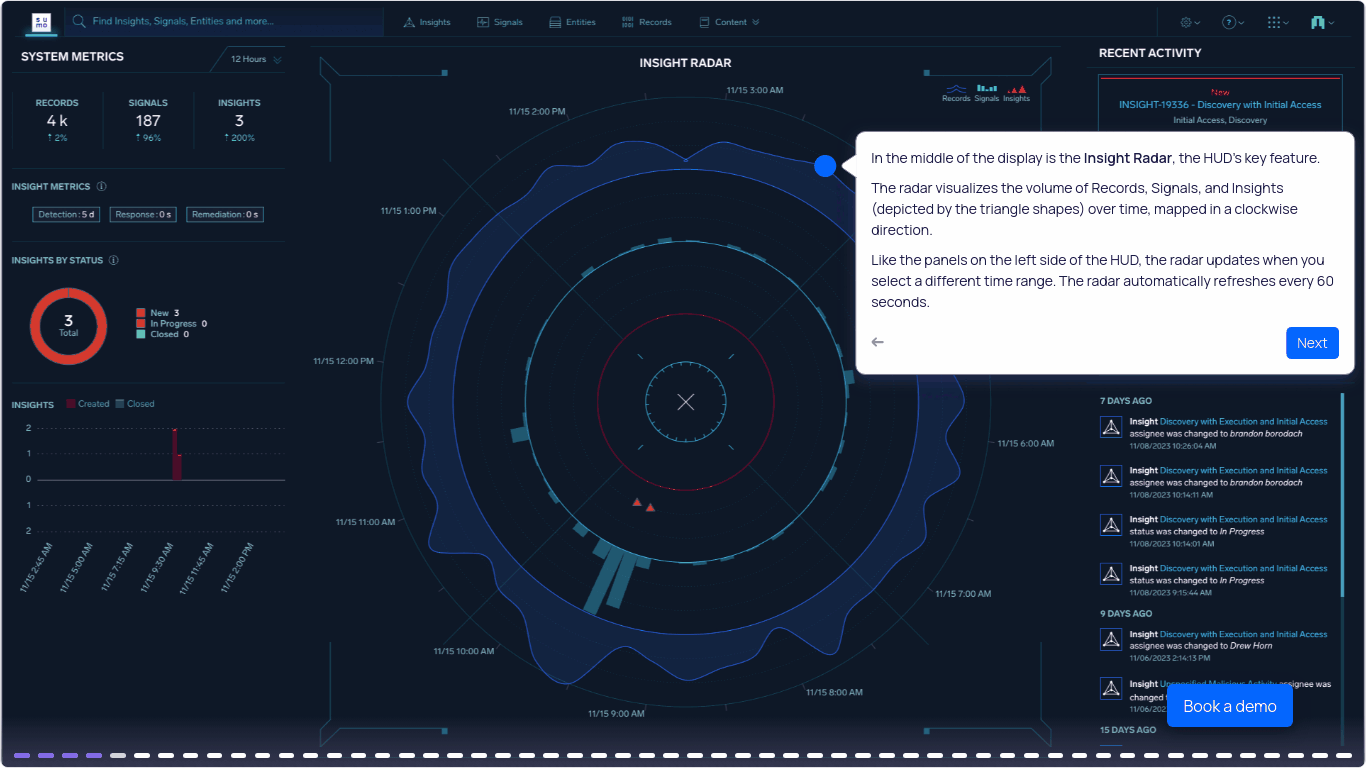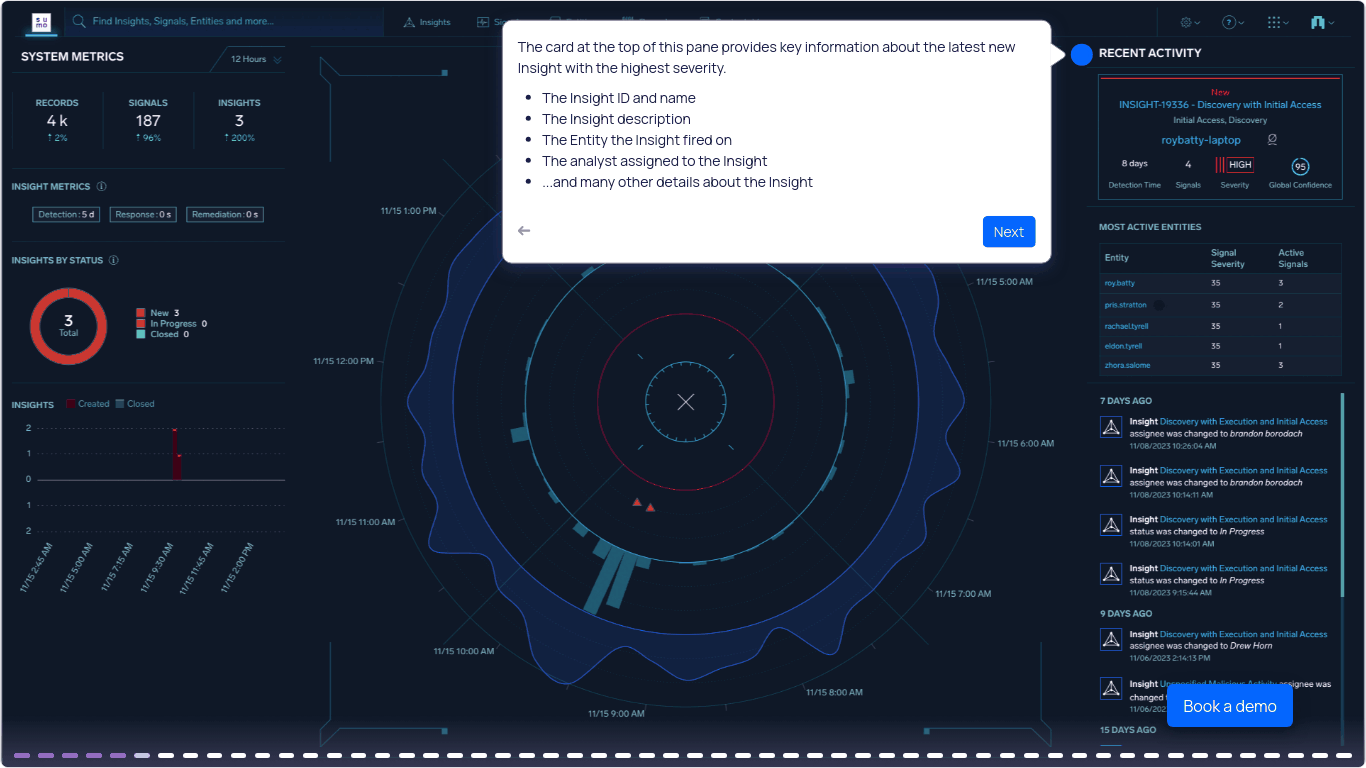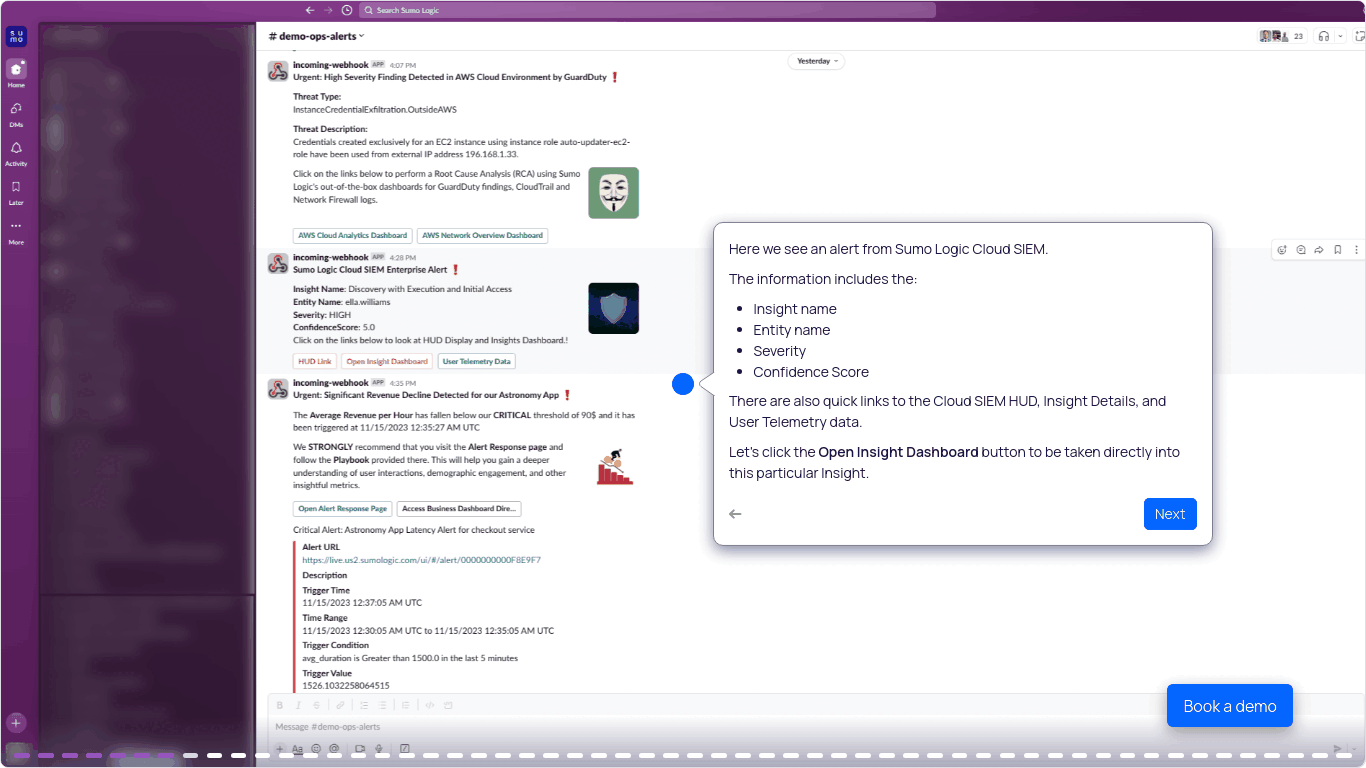
우선 순위 알림 이상의 경험을 제공합니다. 사용자 및 네트워크 컨텍스트가 강화된 실행 가능한 인사이트로 신속하게 위협 사냥하세요.

Cloud native architecture

클라우드 네이티브 아키텍처

필요에 따라 확장합니다. SIEM은 보안 팀의 SOC 효율성을 높이기 위해 멀티 테넌트 확장 및 탄력성을 지원합니다.

UebaBaseline

UEBA 베이스라인 구축

사용자 행동을 빠르게 학습하여 오탐을 줄이면서 스마트하게 이상 징후를 탐지합니다.

ThreatIntelligenceEnrichment

위협 인텔리전스 강화

자체적으로 선별한 피드를 포함하여 신뢰할 수 있는 여러 출처의 위협 인텔리전스가 모든 경고를 상황에 맞게 분석하여 빠르게 조사하고 대응합니다.

Detection as code

코드로 탐지

소프트웨어처럼 탐지 규칙을 관리하고 GitHub와 직접 동기화하세요.

Smarter Analyst

더 스마트한 분석 경험

로그, 탐지 및 자동화 업무를 하나의 일관된 환경에서 작업하세요.

SIEM 소프트웨어는 보안 정보 관리(SIM) 및 보안 이벤트 관리(SEM) 도구의 기능을 결합된 것입니다.

SIM 기술은 다양한 데이터 유형으로 구성된 로그에서 정보를 수집합니다. 이와 대조적으로 SEM은 특정 유형의 이벤트를 더 면밀히 살펴봅니다.

이러한 기술을 함께 사용하면 자동으로 생성된 컴퓨터 로그에서 보안 관련 데이터를 수집, 모니터링 및 분석하는 동시에 여러 소스의 컴퓨터 로그 데이터를 중앙에서 통합 관리할 수 있습니다. 이 종합 보안 솔루션은 공식화된 인시던트 대응 프로세스를 가능하게 합니다.

SIEM 소프트웨어 도구의 일반적인 기능은 다음과 같습니다.

  • 보안 관련 데이터 수집, 분석 및 보고
  • 보안 알림의 실시간 분석
  • 보안 데이터 로깅 및 보고서 생성
  • ID 및 액세스 관리
  • 로그 감사 및 검토
  • 인시던트 대응 및 보안 운영

자세히 알아보기

SIEM은 다음과 같은 몇 가지 주요 기능을 통해 탁월한 인시던트 대응 및 엔터프라이즈 보안 성과를 가능하게 합니다.

데이터 수집 – SIEM 도구는 다양한 소스 및 애플리케이션의 이벤트 및 시스템 로그와 보안 데이터를 한곳에서 집계합니다.

상관관계 – SIEM 도구는 다양한 상관관계 기술을 사용하여 데이터의 일부를 공통 속성과 연결하고 해당 데이터를 SecOps 팀이 실행할 수 있는 정보로 전환하는 데 도움을 줍니다.

알림 – 보안 이벤트 발생을 나타내는 미리 정의된 신호나 패턴이 감지되면 보안 운영팀 또는 IT팀에 자동으로 알리도록 SIEM 도구를 구성할 수 있습니다.

데이터 보존 – SIEM 도구는 대량의 로그 데이터를 저장하도록 설계되어 보안 팀이 시간의 흐름에 따라 데이터를 상관 분석할 수 있게 하며, 초기에 탐지되지 않았을 수 있는 위협이나 사이버 공격에 대한 포렌식 조사를 수행할 수 있도록 합니다.

파싱, 로그 정규화 및 분류 – SIEM 도구는 조직이 몇 주 또는 몇 달 전에 생성되었을 수 있는 로그를 더 쉽게 분석할 수 있도록 합니다. 파싱, 로그 정규화 및 분류(Categorization)와 같은 SIEM 도구의 추가 기능을 통해 수백만 건의 로그 항목을 검토해야 하는 경우에도 로그를 더 쉽게 검색하고 포렌식 분석을 수행할 수 있습니다.

대표적인 SIEM 사용 사례는 다음과 같습니다.

규정 준수 – 규정 준수 프로세스를 간소화하여 데이터 보안 및 개인정보 보호 규정을 준수합니다. 예를 들어, 고객으로부터 신용 카드 정보를 수집하는 판매자를 위한 데이터 보안 표준인 PCI DSS를 준수하기 위해 SIEM은 데이터베이스 내의 네트워크 액세스 및 거래 로그를 모니터링하여 고객 데이터에 대한 무단 액세스가 있었는지 확인합니다.

인시던트 대응 – 인시던트 대응 활동의 효율성과 적시성을 높입니다. 보안 침해가 감지되면 SecOps 팀은 SIEM 소프트웨어를 사용하여 공격자가 기업 보안 시스템을 침해한 방법과 침해로 인해 영향을 받은 호스트 또는 애플리케이션을 신속하게 식별할 수 있습니다. SIEM 도구는 자동화된 메커니즘을 통해 이러한 공격에 대응할 수도 있습니다.

취약점 관리 – 네트워크와 IT 인프라를 선제적으로 테스트하여 사이버 공격의 진입 지점을 탐지하고 대응하세요. SIEM 소프트웨어 도구는 네트워크 취약점 테스트, 직원 보고, 공급업체 발표뿐 아니라 새로운 취약점 탐지에 중요한 데이터 소스입니다.

위협 인텔리전스 – 긴밀하게 협력하여 지속적 지능형 위협(APT) 및 제로데이 위협에 대한 취약점을 줄이세요. SIEM 소프트웨어 도구는 애플리케이션 스택 내에서 생성되는 로그 데이터를 수집하고 분석하기 위한 프레임워크를 제공합니다. UEBA를 사용하면 내부자 위협을 선제적으로 발견할 수 있습니다.

Sumo Logic SIEM은 로그로 구동되는 클라우드 네이티브 다목적 솔루션인 Sumo Logic 보안 플랫폼의 일부입니다. SIEM 외에도 Sumo Logic의 강력한 로그 분석 플랫폼은 인프라 모니터링, 애플리케이션 옵저버빌리티 및 보안용 로그를 지원하여 앱을 모니터링, 문제 해결 및 보안하는 데 도움을 줍니다.

고객들이 Sumo Logic SIEM을 선택하는 이유는 다음과 같은 차별화된 기능 때문입니다:

통합된 단일 로그 분석 플랫폼 – 개발자, 보안, 운영 및 사업부 팀을 위한 단일 통합 솔루션입니다.

클라우드 네이티브 분산 아키텍처 – 로그로 구동되는 확장 가능한 멀티테넌트 플랫폼으로 데이터 손실이 없습니다.

계층화된 분석 및 크레딧 라이선싱 – 데이터 증가 속도에 맞춰 확장되는 유연한 구독을 즐기세요.

머신러닝 및 고급 분석 – 머신러닝을 통해 문제를 더 빠르게 식별, 조사 및 해결하세요.

기본 제공되는 감사 및 규정 준수 – 가장 광범위한 인증 및 증명을 통해 규정 준수를 쉽게 입증할 수 있습니다.

설계 단계부터 보안 – 저희는 인증, 증명, 침투 테스트, 코드 검토 및 유료 버그 바운티 프로그램에 매년 수백만 달러를 투자합니다.